Enterprise cybersecurity has developed around layers of monitoring, detection, and response technologies. But there is a fundamental weakness in that model: organizations frequently have limited visibility into whether their security systems would actually detect a particular attack.
A detection rule may exist without working as intended. A telemetry pipeline may silently fail. Critical logs may never reach the security operations center. These failures can leave organizations unaware of threats that their infrastructure was supposed to identify.
Brava Security is building a platform to help enterprises examine those weaknesses. The company has announced its emergence from stealth with $15 million in funding led by F2 Venture Capital and Pitango VC. The funding was first reported by Axios.
At the center of its offering is multi-agent AI technology that generates the exact telemetry an attack would produce without executing it. The platform uses that information to evaluate existing defenses, identify attacks they would miss, and help correct the underlying gaps.
A Different Starting Point for Cybersecurity Automation
Much of the industry’s current attention is focused on AI agents that can investigate alerts and support security teams. Brava is concentrating on a prerequisite for making those capabilities effective: ensuring that the security infrastructure generates the evidence those agents need.
As enterprises adopt more cloud services, AI applications, and AI-assisted development tools, security teams must manage increasingly complex telemetry environments. More data sources introduce more opportunities for incomplete collection, broken pipelines, and detection rules that fail to recognize relevant activity.
Brava CEO and co-founder Idan Basre says these issues need to be addressed before enterprises can confidently automate security decisions.
“Everyone is racing to put AI in charge of the SOC. You can’t automate a decision based on evidence no one ever proved,” said Basre. “We’re solving the problem that comes before AI can make the right decision: making sure the security infrastructure actually sees the threats it’s supposed to detect.”
His perspective comes from experience in enterprise security products. Before founding Brava, Basre spent ten years in Unit 8200 as a threat researcher and later led product management for Microsoft Defender.
Modeling the Evidence Left Behind by Attacks
Brava’s platform focuses on understanding how attacker behavior translates into telemetry within a specific enterprise environment.
Its Security Operations platform identifies what an attack should look like across available log sources, evaluates whether existing defenses would capture that activity, and identifies the missing detections and data feeds. It can then rewrite SIEM detections and data feeds that fail to recognize the modeled behavior.
The company also emphasizes that its technology generates attack-related telemetry without executing the attack itself. This is central to its approach to evaluating security infrastructure.
Co-founder and CTO Itay Gabbay describes the challenge as understanding the precise relationship between an attack and the evidence it generates.
“The hard part of security was never writing detections. It’s knowing exactly what an attack will look like in a specific environment, across all of its log sources, before it ever happens. That’s the problem our models were built to solve,” said Gabbay.
The platform also investigates alongside security teams, bringing together information to support decisions based on evidence rather than assumptions.
Customer Traction and Deployment Speed
Brava has signed Fortune 100 companies across retail, energy, and hospitality. Its customers also include Cushman & Wakefield and WELL Health, one of Canada’s largest healthcare companies.
The company is positioning compatibility with existing infrastructure as an important part of its enterprise strategy. Its platform integrates with Splunk, Google SecOps, CrowdStrike, and more than 70 other sources and destinations.
Brava reports that its first insights are available within 10–15 minutes of onboarding, allowing organizations to start evaluating their findings without a lengthy deployment process.
At Cushman & Wakefield, CISO Erik Hart described how Brava supports the company’s efforts to use AI in its security operations.
“Our SecOps journey is about applying AI where it makes our people more effective, and Brava sits at the center of that. It investigates alongside our team, bringing evidence together so decisions rest on facts rather than on searching” said Hart.
The Team and Investment Behind Brava
The company’s founding team combines experience in threat research, AI development, and enterprise security. Gabbay spent seven years in the IDF building core AI systems, including work on a joint DARPA-Israeli research program.
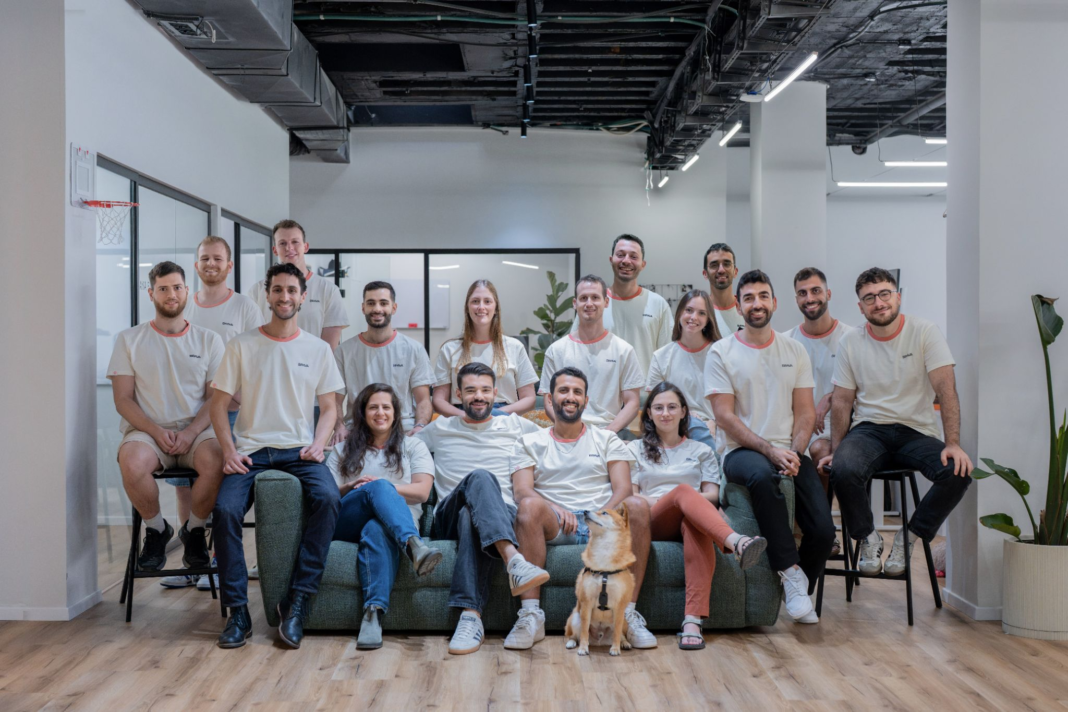
Brava has approximately 20 employees, bringing together AI researchers and security researchers. Its R&D operations are based in Israel, with a commercial team expanding across the United States.
The $15 million seed round included participation from angel investors, including executives from Anthropic, Microsoft, and Check Point, alongside lead investors Pitango and F2 Venture Capital.
Brava plans to use the capital to accelerate technology development and expand its commercial operations across North America. Financial services and government are among the additional markets the company is preparing to pursue.
Making Security Decisions More Reliable
Brava’s emergence comes at a time when enterprises are reconsidering how much responsibility AI agents should take on within security operations. The company is approaching that transition from the perspective of the underlying infrastructure rather than the agents themselves.
Its central proposition is straightforward: security teams need to know whether their defenses can recognize an attack before they can confidently depend on automated systems to investigate one.
By making detection gaps measurable and helping organizations address them, Brava wants to establish a more reliable foundation for the next generation of enterprise security operations.
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.