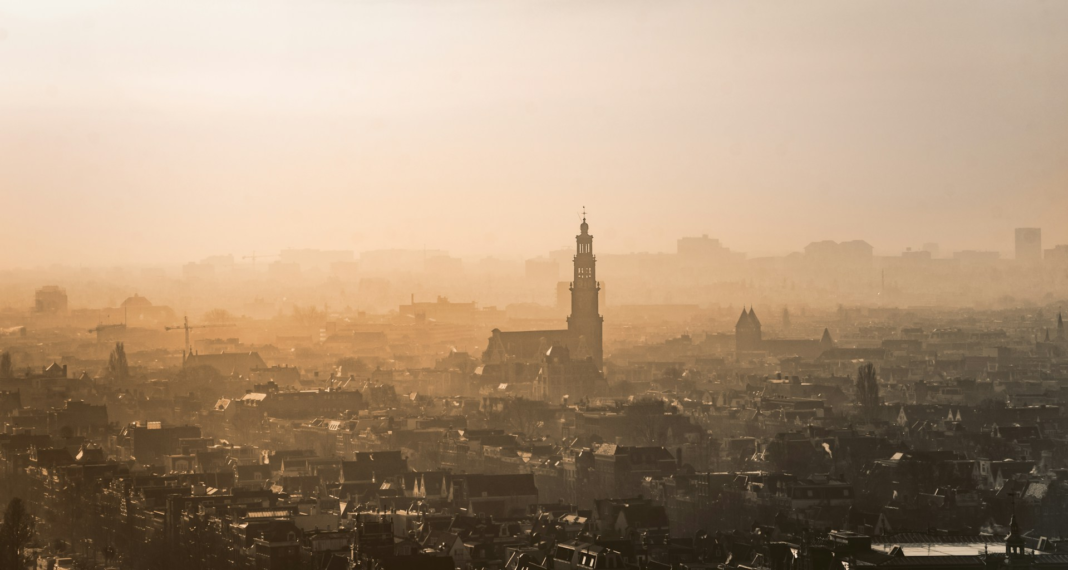
Amsterdam packs an unusual amount into a small city: a global travel platform, a payments company processing for much of Europe, a metro network, a care provider, two universities, and the emergency services region that coordinates when something goes wrong. The six CISOs below secure all of it. What they share is a working environment where NIS2, DORA, and the Dutch healthcare standard NEN 7510 are not abstractions, and where the distance between a security decision and a citizen feeling its effects is very short.
Predrag Vuckovic – CISO, Booking.com
Predrag Vuckovic leads global security at Booking.com, one of the world’s largest digital commerce platforms, a role he took in June 2024 after a year as Senior Director of Group Security, Safety and Resilience. More than two decades of his career have run through regulated finance and payments: nearly six years as CISO of Zalando Payments in Berlin, three as CISO of Eurobank in Belgrade, and six as CISO and head of department at Hypo Alpe-Adria-Bank, where he had started as an IT administrator. His regulatory range reflects that path, covering GDPR, PCI DSS, ISO 27001, SOX, DORA, and the German banking supervision standards BAIT and ZAIT. He frames the job as translating cyber risk into business and financial impact, which is the language a platform serving millions of travellers and partners needs.
Marty Wijnen – CISO, Mollie
Payments leave no room for a security programme that slows things down, and Marty Wijnen has spent his career at companies that could not afford one. CISO of Mollie since September 2023, he secures a payments provider built to serve businesses across Europe and the UK. He arrived from OLX Group, where he was Head of Security EU and then Director of Global Security, and before that spent more than four years as Director of Information Security at Delivery Hero in Berlin. The foundation was eight years at adidas, rising from senior security specialist to Director of IT Security Applications. PCI DSS, risk assessment, application security, and incident response in large complex environments run through all of it. His stated philosophy is people-centric: security as an educator that lets a business move faster rather than a brake on it.
Daniël Wunderink – CISO, GVB
When the metro, tram, bus, and ferry network of a major European city depends on your controls, the operational technology is the point. Daniël Wunderink has been CISO of GVB, Amsterdam’s municipal transport operator, since June 2018, responsible for information security and cybersecurity across both IT and OT: rail, tunnel, power, communications, water management, charge management, safety infrastructure, and autonomous systems. He describes himself as an old-school ethical hacker, and the record supports it, with red and tiger team work running through nearly five years at KPMG and three as Manager of Security and Technology at PwC. His architecture background is in national identity infrastructure, having advised on the Dutch eID frameworks eHerkenning and DigiD and worked on the UK government’s Identity Assurance Programme through Digidentity. He has co-chaired the NL Rail ISAC since March 2023.
Judith Jongeneel – CISO, University of Amsterdam and Amsterdam University of Applied Sciences
Two institutions, one security chief. Judith Jongeneel became CISO of both the University of Amsterdam and the Amsterdam University of Applied Sciences in April 2026, taking on a shared brief across two large, federated, and famously open academic environments. She arrived from Deloitte, where she spent four and a half years in cyber strategy and transformation, rising from senior consultant to manager. Before consulting came national security policy: more than two years as an adviser on cybersecurity collaboration at NCSC-NL, the Dutch national cyber security centre, in The Hague, and before that an information advisory role at BECIS. Universities sit at an awkward intersection of research openness, student data, and NIS2 obligations, and her combination of national-level coordination and transformation consulting reads as built for it.
Jelte van der Maat – CISO, Cordaan
Healthcare data carries obligations most sectors never encounter, and Jelte van der Maat has spent the last few years inside them. CISO of Cordaan since October 2025, he secures a provider delivering nursing, care, and support to people of all ages across Amsterdam. He came from iHub, the education and family care organisation, where he served as both CISO and Chief Privacy Officer, having progressed from privacy officer through information security officer over three years, working to GDPR and NEN 7510, the Dutch standard for information security in healthcare. His earlier career is unusual for this list: seven years as data manager at the International School of Amsterdam, and nearly a decade running his own studio designing gamification, serious games, and alternate reality experiences. Care organisations need security explained to non-technical staff at every level, and few CISOs arrive with that much practice at making complex systems legible.
Jan F. Bakker – CISO, Veiligheidsregio Amsterdam-Amstelland
Jan F. Bakker secures the organisation that coordinates when Amsterdam has a crisis. CISO of Veiligheidsregio Amsterdam-Amstelland since October 2024, after a year as its information security officer, he works for the regional safety body in which municipalities, the fire brigade, medical services, police, and the public prosecution service cooperate. His background is financial crime rather than infrastructure: nearly two years in customer due diligence at Adyen, working across KYC and OSINT, followed by an information security officer role at Breinstein. He has served as a reservist with the Royal Netherlands Navy since December 2025, and sits as treasurer and board member of a residents’ association representing 1,200 members in a social housing and student complex in the west of the city.
What This Group Says About Amsterdam
Amsterdam’s security leadership is defined less by scale than by proximity. The same city holds a platform serving millions of travellers, a payments provider moving money across a continent, and the people responsible for keeping trams running and care records private. These six arrived from ethical hacking, national cyber policy, financial crime investigation, Big Four consulting, and in one case game design, and they converge on a shared requirement: making security decisions that hold up when the people affected live down the road.
Amsterdam is one stop in an ongoing series profiling the security leaders shaping their cities and sectors. Explore the rest below.
- Signed, Sealed, Secured: Newly Appointed CISOs to Watch
- Berlin’s Security Chiefs to Watch: The CISOs Behind Its Tech
- Paris’s CISOs to Watch: Leaders Securing France’s Top Brands
- Cybersecurity Leaders to Watch in London: Securing Britain’s Business Capital
- Chicago’s CISOs to Watch: Security Leadership Citywide
- Securing the Skies: Aviation’s Top Security Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.