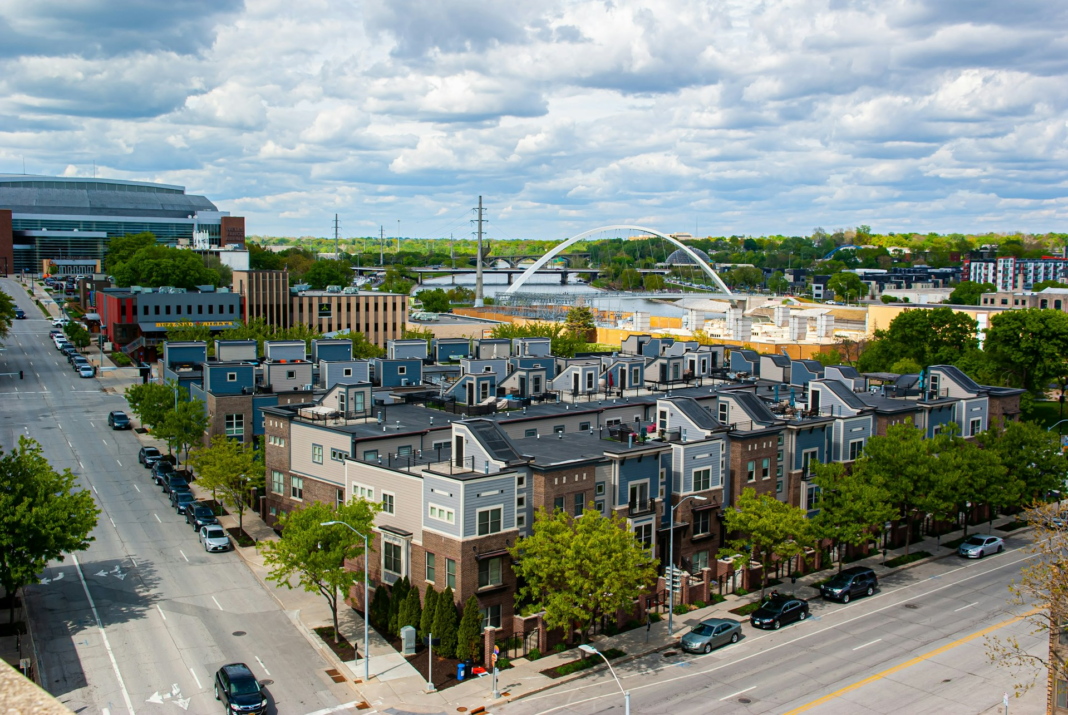
Three of the four leaders below worked at Principal Financial Group at some point, and two of them came to security through internal audit. Des Moines is an insurance and financial services town, and its cybersecurity community reflects that: heavy on risk management, audit, and compliance, with people who tend to spend a decade or more at the same employer. The exception is a trucking company’s security chief who built a program from nothing and runs the data centers too.
Marty DeDecker – CISO & Director of Infrastructure Services and Operations, Ruan Transportation
Marty DeDecker spent 18 years at Principal Financial Group, including a year in IT auditing where he partnered with five global subsidiaries on Y2K planning and risk mitigation. He later ran business application development for the company’s health insurance division with 65 direct reports and a $6.5 million budget, then spent 12 years as Assistant Director of Information Services delivering corporate messaging and collaboration systems. After two years directing IT service delivery at Aviva USA and a year handling the separation and merger that created Athene, DeDecker joined Ruan Transportation in September 2014. He built the company’s security program from the ground up and continues to mature it, while also running data center facilities, servers, storage, virtual desktop infrastructure, and the IT service desk. Ruan operates a nationwide data network supporting hundreds of local operations, and DeDecker’s teams keep it running.
Ben Meader – Director, Information Technology Security, EMC Insurance Companies
Ben Meader co-presented a security framework called DREAMR at the 2014 RSA Conference. He started his career as a help desk assistant at Iowa State, then spent eight years at Hewitt Associates as a product manager and network security engineer. Three years at Arthur J. Gallagher followed, where he led a global data privacy initiative and served as technical lead for web proxy, laptop encryption, and vulnerability scanning. Meader returned to Des Moines in 2011 for security analyst work at Athene, then spent nearly eight years at Principal Financial Group leading the security review and consulting team and later serving as Assistant Director of IT. He has been Director of Information Technology Security at EMC Insurance since November 2021, directing cybersecurity operations and engineering, identity and access management, and technology assurance services. He has held a CISSP since 2012 and holds an MBA from DePaul. Outside EMC, he founded Ingamix in April 2026 to build a QR-driven fan engagement platform for live sports venues, an idea that started at a Startup Weekend Des Moines event.
Christopher Garza – Director of Information Security, Farm Bureau Financial Services
Auditing is where Christopher Garza learned the business. He started at KPMG in Des Moines as an intern in 2011 and spent more than two years there as an advisory associate and senior associate, evaluating financial IT controls for SOX compliance and conducting SSAE16 and SOC1 audits for financial and insurance clients. He joined Farm Bureau Financial Services in 2015 as an IT auditor, then spent a year and a half as a senior IT auditor covering everything from mainframe access controls to business continuity planning. Garza moved into security in 2019 as Lead Information Security Analyst, building a governance, risk, and compliance program and creating a security risk register mapped to the NIST Cybersecurity Framework. He became Information Risk Manager in 2021 and Director of Information Security in August 2023.
John Baldwin – Cybersecurity Director, Pella Corporation
John Baldwin has worked at Pella Corporation for 25 years. He spent his first 17 as an IT manager before moving into security in December 2018 as Enterprise Cybersecurity Manager, then Senior Manager of Cybersecurity and GRC, and since October 2024 as Cybersecurity Director. He runs the window and door manufacturer’s enterprise cyber risk management program using a Zero Trust approach, providing security guidance across the business. Baldwin describes cybersecurity as a public health function and makes a point of sharing what works and what does not with peers across industries.
Risk People Running Security
The path through audit and risk management is unusually well worn here. Garza spent seven years auditing IT systems before anyone made him a security analyst. DeDecker did a year of IT auditing at Principal that led into two decades of infrastructure and service delivery leadership. Meader has spent his career translating security risk into business terms for insurers and consultancies. Baldwin came at it from the other direction entirely, running IT at a manufacturer for 17 years before the company built a cybersecurity function around him. In a metro where insurance and financial services dominate the employer list, the people running security tend to think in risk registers and control frameworks first, which is what those industries require.
Discover more CISOs securing their organizations:
- Albany’s Cybersecurity Leaders to Watch
- Providence’s Cybersecurity Leaders to Watch
- Built to Last: Winnipeg’s Cybersecurity Leaders to Watch
- Half a Million Neighbours: Wellington’s Cybersecurity Leaders to Watch
- At the Edge of the Map: Auckland’s Cybersecurity Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.