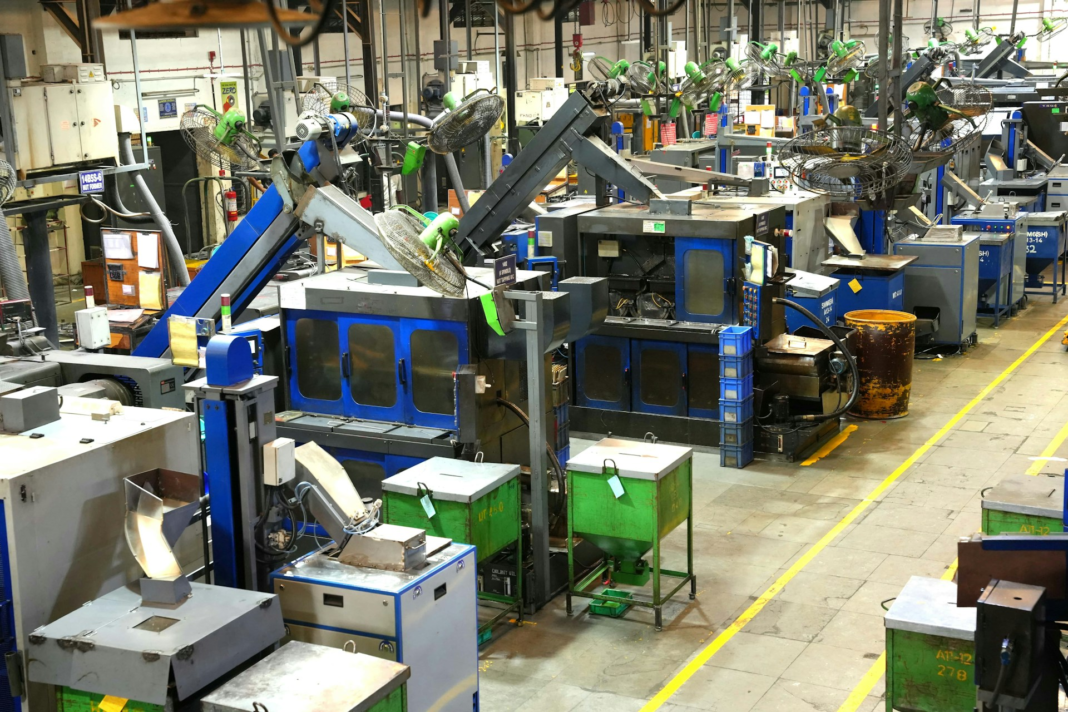
Machinery manufacturers build the tractors, pumps, generators, and industrial equipment that keep farms, cities, and factories running, and their plants, connected products, and global supply chains make them prime targets. The seven CISOs below protect some of the best-known names in American manufacturing, and their routes into security are as varied as the machines their companies build. One served as a Marine sergeant with the 1st Marine Division. Another managed IT at a round-the-clock window manufacturing plant before spending more than two decades leading security at Honeywell and John Deere. A third built Goldman Sachs’s control program for algorithmic trading, and a fourth introduced the first IP-based network in Upstate New York.
James Johnson – VP & CISO, John Deere
James Johnson started as IT manager at a Pella Corporation window plant in Story City, Iowa, serving on the plant manager’s leadership team and running IT and computerized production systems for a 24/7 manufacturing facility. He spent 11 years at Honeywell, rising from information security specialist through security risk management roles to CISO of the Automation and Control Solutions division, a $16 billion business with 70,000 employees in more than 100 countries, and later CISO and director of business enablement on Honeywell’s corporate global security leadership team. Johnson joined John Deere as CISO in 2014 and was named VP and CISO in November 2023. His focus areas include cyber resilience, supply chain security, and cybersecurity regulation.
Winthrop (Andy) Welch – CISO, AGCO
Winthrop (Andy) Welch began as a business analyst at American Cyanamid and spent 17 years at KPMG, delivering security programs for financial services and government clients and supporting post-breach recovery for academic medical centers including NYU Medical Center and Columbia University. At Goldman Sachs he built the firm’s Automated Trading Control program for algorithmic trading oversight, then served as an associate partner in IBM’s security and risk consulting practice, providing virtual CISO leadership to major financial institutions. At Yahoo he built and led the global IT security GRC function, served as cybersecurity lead on its AI/ML task force, and created security analytics supporting more than $5 billion in M&A activity. After a year as a fractional CISO, Welch became CISO of AGCO in January 2026.
Brent Ball – CISO, Dover Corporation
Brent Ball started in IT risk management and forensics at Nationwide Insurance and Chase, then managed security technology engagements at EY and led global security investigations at TransUnion. At Baxter International he received the CEO Award for leading its “cyber pandemic prevention” program and cut security program overhead by 93%. He led the security buildout for Baxalta’s $31 billion spin-off, achieving an early exit from its transition service agreement, and served as interim CISO at Shire. At Takeda he rose to VP of information security, leading more than 100 professionals and a budget of over $50 million across threat management, security operations, manufacturing and lab security, and AI governance. Ball became CISO of Dover Corporation in September 2025.
Timur Qader – VP & CISO, Xylem
Timur Qader spent nearly 12 years at Verizon, where he introduced the first IP-based network in Upstate New York and helped build the Verizon Wireless program management office. At GLOBALFOUNDRIES he led global security and US IT, achieving global ISO 27001 certification, building the company’s first 24/7 command center, and cutting $23 million in expenses, before becoming global CISO and reporting to the board’s risk committee. After serving as executive director at the Center for Internet Security, he became VP and global CISO of Resideo, later adding enterprise IT to his remit. Qader became VP and CISO of Xylem in August 2026. A three-time CISO, he is also a published author, speaker, and board advisor on cybersecurity and AI governance.
Ralph Carey – CISO & VP Cyber Security, Terex Corporation
Ralph Carey worked as a systems engineer at Sycamore Networks and Mercator Software before joining Terex Corporation in 2003 as network systems manager. Over more than two decades there, he built global security and privacy controls, became director of information security, and was named CISO and VP of cyber security in 2019. He has grown Terex’s cybersecurity capability from an early-stage function into a board-governed program embedded in enterprise risk management, improved its external cyber risk ratings by 35%, and built a team across the US, Europe, and Australia with no voluntary turnover. He also reviews the company’s 10-K cybersecurity disclosures with legal and leads incident response with executives and outside forensic partners. His operating principle is “No, but”: when an initiative carries too much risk, he redesigns it so the business can still move forward.
Heather Hausmann – EVP, CIO & CISO, Pentair
Heather Hausmann began as a system administrator at Sit Investment Associates and worked in security roles at EY, Digital River, SUPERVALU, and Medica Health Plans. At Ameriprise Financial she rose from director of information security to VP of technology, then returned to SUPERVALU as VP and CISO. After serving as information security officer at RSM and CISO of SPS Commerce, she joined Pentair as CISO in 2022 and also took on IT infrastructure. Hausmann became CIO and CISO in 2024 and was elevated to executive vice president in March 2026, leading digital transformation and security across the enterprise.
William Cummings – VP, CISO & Product Security Leader, Generac Power Systems
William Cummings served four years as a sergeant in the US Marine Corps, deploying twice with the 1st Marine Division. He worked as a help desk manager and UNIX administrator at the University of Wisconsin-Milwaukee, then in security and IT audit at Deloitte and PwC. At Johnson Controls he led global IT audit and the company’s cyber security improvement program, and as VP and CISO of Adient he built a 40-person global security organization for the $17 billion spin-off, separating OT networks across more than 200 plants and standing up a 24/7 SOC. As CISO of REV Group, he also led IT infrastructure and technology integration for more than $250 million in M&A. Since joining Generac in 2022, Cummings has built its cybersecurity program from the ground up, establishing IEC 62443 product security for connected energy devices, segmenting OT networks across global plants, consolidating identity across more than 20 domains, and launching AI governance and a security champions program.
Securing the Machines That Build the World
These seven CISOs show the range of experience behind manufacturing security. Johnson, Carey, and Hausmann have built long careers inside the industry, while Welch, Ball, and Qader brought experience from finance, pharmaceuticals, and semiconductors. Cummings carried a Marine’s discipline into OT and product security. As factories and products become more connected, these leaders keep the machines and the people who rely on them secure.
Discover more CISOs securing their organizations:
-
- Campus Defenders: Australia’s Higher Education Cybersecurity Leaders to Watch
- Connected Nation: Germany’s Telecommunications CISOs to Watch
- Alpine Assurance: Switzerland’s Insurance CISOs to Watch
- From High Street to Basket: The UK’s Retail Cybersecurity Leaders to Watch
- Serving the States: Australia’s Government CISOs to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.