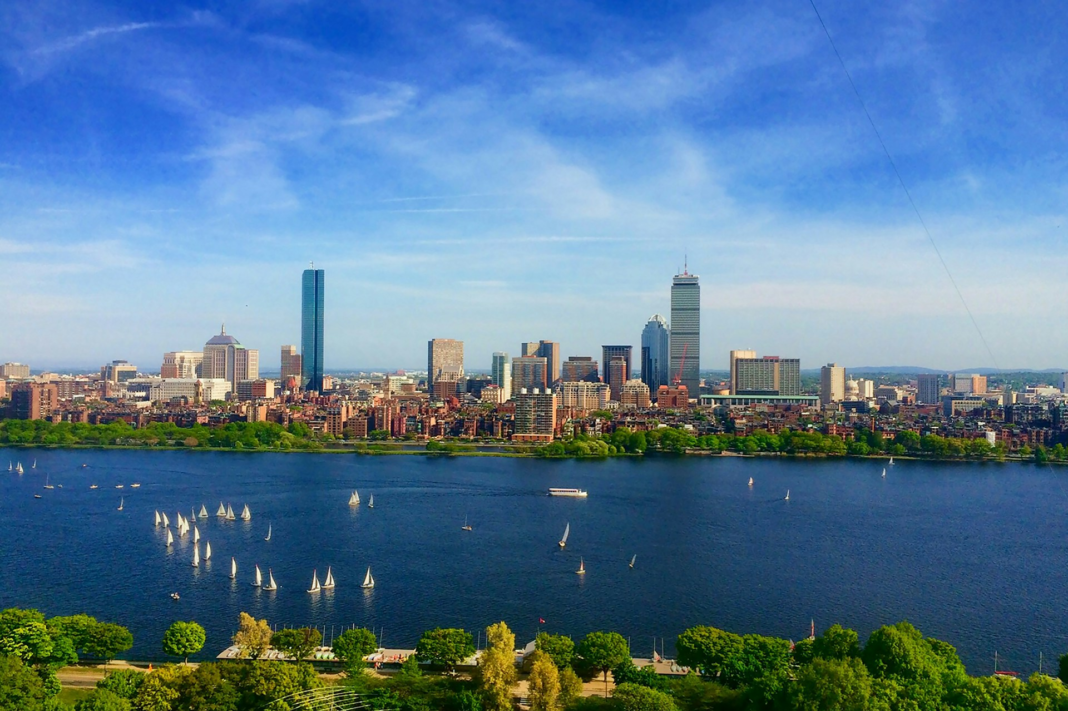
Boston runs on three industries that all handle data other people cannot afford to lose: hospitals, universities, and software. The seven leaders below work across all three, plus insurance and industrial manufacturing. Several have spent their entire careers within a few miles of each other, moving between Harvard, Mass General Brigham, Boston University, and UMass, and several more came up through engineering rather than governance. It is a bench with unusual technical depth and unusually long institutional memory.
Tony Arous – SVP and CISO, Toast
Tony Arous became SVP and CISO of Toast, the restaurant technology platform, in June 2026. He arrived from Twilio, where he served two and a half years as CISO, and before that spent seven years at Autodesk, rising from Head of Application Security to Chief Security Officer, leading an organisation of more than a hundred people and reporting quarterly to the board and audit committee. His approach is engineering-first rather than policy-first: at Autodesk he built in-house software for static analysis, software composition, and cloud security posture management, established the company’s first security architecture function, and created a security data science program delivering analytics and anomaly detection across a portfolio of more than 2,000 services. He began as a software engineer at EMC, where he spent eleven years, finishing as senior manager of product security. He advises Craft Ventures’ CISO advisory council and is a founding member of the Okta CISO Forum.
Esmond Kane – CISO, Advarra
Esmond Kane has spent two decades securing organisations where research, healthcare, and regulation intersect. CISO of Advarra, the clinical research compliance company, since September 2024, he previously spent five years as CISO and Vice President at Steward Health Care, leading a forty-person team and a $10 million budget across a multi-state and international footprint. Before that he was Deputy CISO at Mass General Brigham, where he launched the information security program, established a hybrid security operations centre, and led the response to multiple critical incidents and data breaches. His foundation was seventeen years at Harvard, where he served as Director of IT Security for Policy, Risk and Compliance, ran the university-wide vulnerability assessment and code analysis service, and earlier led incident response investigations for the Faculty of Arts and Sciences. He advises Bain Capital Ventures, Tenable, and Black Kite.
Bruce A. James – VP and CISO, Boston Children’s Hospital
Bruce A. James became VP and CISO of Boston Children’s Hospital in August 2025, responsible for cybersecurity strategy across a federated IT environment and serving as strategic advisor to the executive team, audit committee, and board of trustees. He came from Intermountain Health, where he spent nearly seventeen years and rose through every level of the security organization: identity and access management team lead, then manager, then director of cybersecurity architecture, then associate and deputy CISO. He also served four months as interim CISO following the retirement of the long-standing incumbent, maintaining program continuity and handing over to the successor. Before healthcare he was CISO and senior software engineer at InterComputer Corporation, leading identity management, key management infrastructure, and PKI development.
Wil Khouri – Assistant Vice Chancellor and CISO, UMass Boston
Wil Khouri has led information security at the University of Massachusetts Boston since 2019, and has been at the institution more than thirteen years in total. He is accountable for governance, oversight, and management of all information security and compliance functions, including the security operations centre, and built the university’s security programme from policy development through zero trust and identity management. Before taking the security title he spent six years as Assistant Vice Provost for Communications and IT Infrastructure Services, giving him budget and operational authority over the estate he now defends. His earlier career spans a decade as Director of Systems and Technology at Boston University, an SVP and CIO role at an international consumer goods company, and a stint as CIO of City Year across thirteen geographically dispersed sites.
Jasvinder Khera – CISO, John Hancock
Jasvinder Khera has been CISO of John Hancock since April 2024, having joined as Senior Director of Cyber Defense in 2022 and built global security teams spanning application security, incident response, vulnerability management, IAM, network security, and monitoring. He came from the Federal Reserve Bank of Boston, where he spent eight and a half years, finishing as Information Security Manager. There he led the security design, architecture, and implementation of the Main Street Lending Program, the largest emergency lending facility ever created in the United States, and assessed the cyber resilience of a critical system processing $13 trillion in daily transactions. He also hosted the Boston Fed’s cybersecurity conferences and convened a threat sharing group for senior leaders at New England depository institutions. Earlier he consulted at Deloitte UK and CGI, including security accreditation work for the UK Ministry of Defence.
Oyefunke Fayoyin – CISO and CIO, Devo
Oyefunke Fayoyin holds both the security and technology seats at Devo, the security analytics company, a dual role she took in May 2025. She owns enterprise security strategy end to end across IT, identity and access management, product security, and risk and compliance, and describes herself as customer zero for the company’s own product, which keeps the programme honest about what works in practice rather than on a roadmap. She came from Lamb Weston, where she was Head of Global Cybersecurity Governance, Risk and Compliance, and before that led application, cloud, and vulnerability management programs as a senior product security manager. Her foundation was nearly five years at Cummins as a cybersecurity and compliance principal working across SOX, PCI, and HIPAA. She is a member of T200, the women’s technology leadership network, and served as VP of Finance for the Austin chapter of Women in CyberSecurity.
Mike Nichols – VP and CISO, CIRCOR International
Mike Nichols became VP and CISO of CIRCOR International, the flow control products manufacturer, in July 2023, having returned to the company earlier that year as senior director of IT security, risk, governance and compliance. He had previously spent three years at CIRCOR as IT compliance manager and then senior manager for security, risk and compliance, working across NIST 800-53 and 800-171, SOX, GDPR, incident response, and business continuity. In between he spent nearly three years at Raytheon Missiles and Defense as a cybersecurity manager and principal for compliance, bringing defense-grade practice back to industrial manufacturing. His grounding is in audit: senior IT auditor at MFS Investment Management, IT auditor at Homesite Insurance, and IT assurance at Wolf and Company, after starting as a systems analyst and engineer in healthcare.
What This Group Says About Boston
Boston’s security leadership is built on institutions rather than industries. Harvard, Mass General Brigham, Boston University, UMass, and the Federal Reserve Bank of Boston all appear in these careers, and several of these leaders moved between them before landing where they are now. That produces a particular kind of CISO: one who has defended open research networks, regulated patient data, and critical financial infrastructure, often in the same city, sometimes in the same decade. The software names on this list, Toast and Devo, are staffed by people who came up the same way. The city trains its own.
Discover more cybersecurity leaders:
-
- CISOs to Watch in Atlanta: From City Hall to the Credit Bureau
- CISOs to Watch in Dallas-Fort Worth: From the Flight Line to the Boardroom
- Vancouver’s CISOs to Watch: From Campus to Cloud
- CISOs to Watch in Denver: From City Hall to the Fortune 500
- Seattle’s CISOs to Watch: Security Leadership Across the Sound
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.