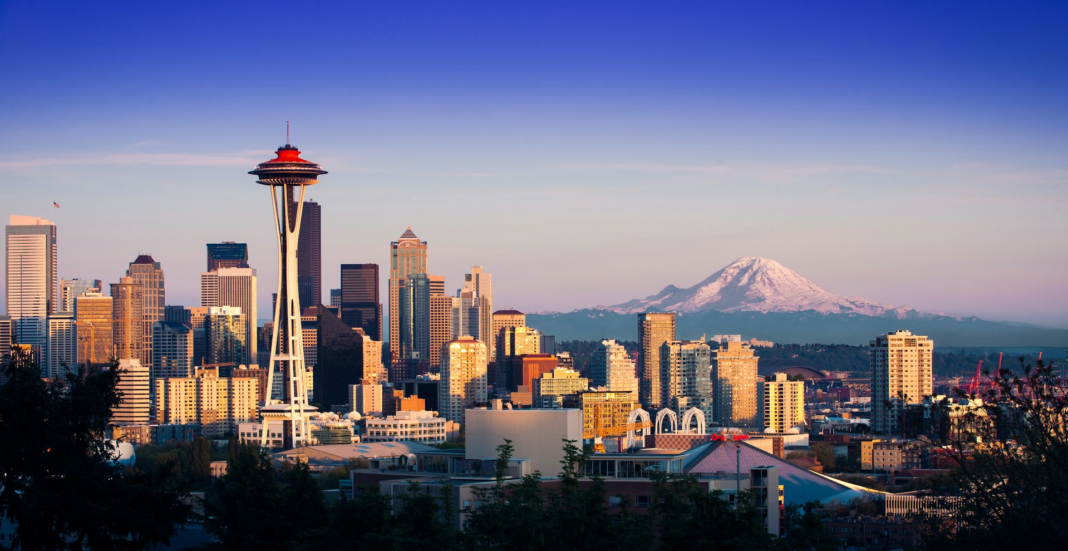
Seattle built the cloud, and the rest of the region’s economy now runs on it: a department store chain founded in 1901, an airline connecting the West Coast, a forest products company more than a century old, a light rail network under construction, and a truck manufacturer in Renton. The CISOs below secure that spread. Several came up through Microsoft, Amazon, or Starbucks, which gives the group an unusual density of shared institutional grounding, and several now apply it to industries that have nothing to do with software.
Mike Hughes – SVP and CISO, Nordstrom
Mike Hughes has spent his career securing the places people shop. SVP and CISO at Nordstrom since March 2025, he arrived from REI, where he spent nearly four years as divisional VP and CISO accountable for security engineering, IAM, GRC, cyber defence operations, and privacy. Before that came two years at Target, first leading the cyber fusion centre’s 24×7 incident response, forensics, insider threat, malware reverse engineering, and hunting teams, then running a broader portfolio spanning network, endpoint, and cryptographic services. The foundation was six and a half years at Starbucks, where he built the company’s first cyber security operations team and matured its global security engineering and application security functions, having started there as a DevOps manager on the Starbucks.com and mobile platform. He describes his mission as bringing honesty, transparency, and integrity to the security function.
Chris Dalton – VP and CISO, Weyerhaeuser
Chris Dalton is a rebuilder. VP and CISO of Weyerhaeuser since April 2019, he has advanced the forest products company’s NIST CSF maturity scores by 45 percent as measured by third-party assessment, deployed zero-trust architecture including SASE and advanced IAM, isolated critical operational technology environments, and delivered a million dollars in budget-neutral efficiencies through tool consolidation. His twenty-five years span high-tech, manufacturing, healthcare, and government. He directed FedRAMP certification at ServiceNow and achieved ISO 27001, SOC 2, and HIPAA certifications there, secured the cloud portfolio at VMware, and served as CISO of Group Health Cooperative. He also built quantitative risk frameworks at Enterprise Holdings, replacing subjective assessment with statistical modelling, and began his security career as an information security officer at the Department of Veterans Affairs.
Alex Di Giacomo – CISO, Sound Transit
Few security leaders can say they designed the SCADA system before they were asked to defend one. Alex Di Giacomo has been CISO of Sound Transit since February 2016, running the information security programme for the agency building and operating light rail, commuter rail, and express bus across the central Puget Sound region, with cybersecurity integrated into multi-billion-dollar, long-term infrastructure programmes. His twenty-six years began in engineering: a decade at Douglas County PUD, first as a control systems electrical engineer and then as its cyber security officer, where he wrote the district’s first cyber security policy to meet NERC CIP standards. Consulting at Accenture on smart grid security and four years at Avanade running IT security services and ISO 27001 governance followed. He holds CISSP, CISM, CISA, CRISC, CDPSE, and C|CISO, and describes investing in people as a core pillar of his leadership.
Grant Bugher – VP and CISO, Outreach
Grant Bugher has built product security functions from nothing at three companies. VP and CISO of Outreach since April 2025, after four years rising through platform security and senior director roles, he owns the security roadmap, budget, and KPIs for the AI sales automation platform, maintaining ISO 27001, ISO 27701, SOC 2 Type II, HIPAA, and ISO 42001 compliance across a multi-cloud environment spanning AWS, GCP, and Azure. He came from Twitch, where as head of product security he replaced a review-checkpoint model with a full security lifecycle and drove known severity 1 and 2 vulnerabilities from over 200 to zero. Before that he spent more than thirteen years at Microsoft, owning the Security Development Lifecycle programme for online services, leading security architecture for Microsoft 365, Azure, and Bing, and developing the reference architecture for Microsoft’s Sovereign Cloud programmes. He also advised ISC2 on CSSLP exam questions.
Peter Oehlert – CISO, Xsolla
Peter Oehlert came up at the intersection of security and software development, and he has stayed there. CISO of Xsolla since September 2025, he secures a video game commerce platform operating across more than 200 geographies and a thousand payment methods. He arrived from Highspot, where he spent five years as Chief Security Officer, and before that led security engineering at Smartsheet, supporting FedRAMP, SOX, SOC, and ISO compliance while personally identifying and shepherding fixes for more than a dozen critical vulnerabilities. Earlier he was Director of Product Security at Facebook and Technical Vice President at iSEC Partners, running an office doing analysis, threat modelling, code review, and tool creation. The foundation was seven years at Microsoft as a software engineer and then security software engineer, plus a stint co-founding a startup as CTO.
Brian Talbert – Managing Director and CISO, Alaska Airlines
Brian Talbert secures an airline from inside the network he spent years building. CISO of Alaska Airlines since October 2022, he oversees technological safeguards and governance while meeting PCI requirements alongside TSA and FAA compliance obligations, and sits on the boards of the Aviation 4 America Cybersecurity Council and the Aviation-ISAC. He had already spent nearly eight years at the carrier as Director of Network and Connectivity Solutions, shaping data networks, unified communications, and network security, and lifting team engagement from below 65 percent to over 95 percent. Before Alaska came a year and a half managing network deployment at AWS, nearly seven years as Senior Manager of Global Networks at Life Technologies, and network security engineering roles at Verizon Business and UUNET. He has also authored and edited technical books on SQL Server, Windows NT, and TCP/IP.
Joshua Carlson – CISO, PACCAR
Joshua Carlson became CISO of PACCAR in January 2026, taking global information security responsibility for the truck manufacturer behind Kenworth, Peterbilt, and DAF, covering strategy, investigations, forensics, policy, risk assessment, and project management across all locations. He has spent a decade at the company, running global security operations teams across North America and Europe, owning disaster recovery, and then serving two and a half years as Director of IT for PACCAR Financial, an operational detour that put him closer to the business. Before manufacturing came nearly eight years at the University of Washington, where he built an information security programme for the Radiation Oncology Center covering vulnerability management, security reviews, and business continuity. Earlier he served three years in the US Army as a signal officer, managing communications networks for coalition forces of ten thousand personnel.
What This Group Says About Seattle
The Seattle bench is shaped by proximity. Microsoft, Amazon, Starbucks, and Nordstrom appear repeatedly in these histories, not as destinations but as training grounds, and the people who passed through them now run security at a railway, a sawmill operator, a truck plant, and an airline. The region exports security leadership into industries the cloud only recently reached, and these seven careers show what that transfer looks like in practice: platform-scale habits applied to operational technology, physical assets, and safety-critical systems.
Seattle is one stop in an ongoing series profiling the security leaders shaping their cities, states, and sectors; explore more features from Washington below.
- CISOs to Watch in Washington’s State Government
- CISOs to Watch in Washington’s City and County Government
- Cybersecurity Leaders to Watch in Washington’s IT Industry
- Cybersecurity Leaders to Watch in Washington’s Defense & Aerospace Industry
- Cybersecurity Leaders to Watch in Washington’s Healthcare Industry
- Cybersecurity Leaders to Watch in Washington’s Higher Education Industry
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.