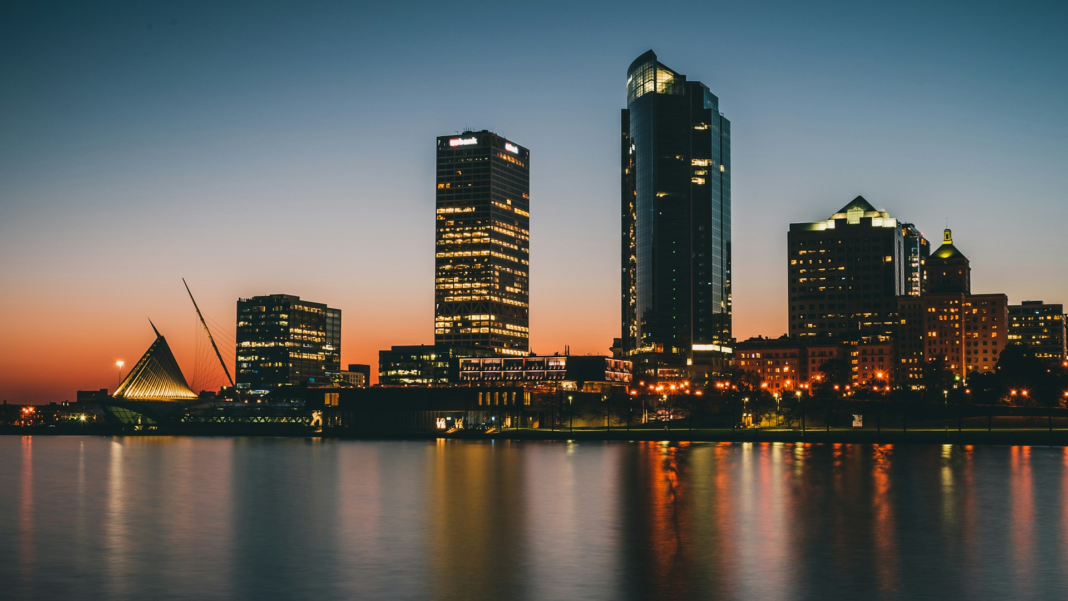
Milwaukee builds things, and a surprising number of its cybersecurity leaders learned their trade on the industrial side. One of the five below ran IT for a crane manufacturer for more than a decade. Another spent 15 years in IT at a plastic film maker after leaving the Army as a military intelligence officer. A third managed SAP for an automation company before taking on security for a retailer and then a power tool maker. The other two came through health care infrastructure and, unusually, through patent law. They now protect a regional energy utility, a large health system, a tool manufacturer, a financial services company, and a life sciences services firm.
Mary Beth Lewis – Director, Enterprise Security and Compliance, WEC Energy Group
Mary Beth Lewis spent more than a decade as IT Director at Morris Material Handling, reporting to the VP of finance and running everything from telecom contracts and manufacturing systems to system security. When Konecranes, which owns Morris, expanded her role, she became global business application support manager. She joined We Energies in 2010, leading database work and later serving as infrastructure manager for five years. Lewis moved into security in 2017 as Director of Technology Security and Compliance at WEC Energy Group, and has led enterprise security and compliance there since May 2021. Her remit spans IT and OT cybersecurity, data security, and physical security for the utility. She started her career leading technical support for a software company serving more than 600 customers.
Chris Stucker – AVP, Cybersecurity (Deputy CISO), Froedtert ThedaCare Health
Chris Stucker served nearly eight years as a U.S. Army military intelligence officer before moving into industry. He spent 15 years at Applied Extrusion Technologies, working through server, network, and security roles to IT manager, then led IT and information security for the Americas at Taghleef Industries. Identity became his specialty. He ran the IAM program at the University of Utah for more than six years, then directed identity and access management at Thomas Jefferson University Hospitals and at Banner Health, where he led a team of 56. Stucker joined Froedtert ThedaCare Health in 2024 as Deputy CISO and was named Associate Vice President of Cybersecurity in September 2026, working remotely. He leads identity strategy across a federated Microsoft environment, including phishing-resistant MFA, and built a workforce development program covering seven security teams. He also teaches in Southern Utah University’s master’s program in cybersecurity and information assurance.
Ray Farrell – VP, Enterprise Security & Infrastructure, Milwaukee Tool
Ray Farrell spent nearly eight years as an integration manager at TIP Technologies before joining Rockwell Automation in 2003. He worked there as a project manager for close to eight years, then managed SAP technical services, overseeing four managers and more than 55 staff across basis, database, monitoring, and development teams. At Kohl’s he ran Unix and SAN delivery, then disaster recovery, then IT service delivery. He spent five years as the retailer’s Director of Information Security. Farrell joined Milwaukee Tool in 2022 as Director of Digital and Information Security and has served as Vice President of Enterprise Security and Infrastructure since March 2024. He holds a PMP.
Lisa Brzycki – VP, IT Risk Management & Office of the CISO, Northwestern Mutual
Lisa Brzycki began her career as a patent agent and IP portfolio manager at Foley & Lardner, drafting and prosecuting patents in areas including industrial automation software, microprocessor design, and medical imaging. She co-founded Talon Software Systems, which built IP portfolio management software for law firms, universities, and corporations. Brzycki then spent a decade as Chief Compliance Officer and Global VP of Legal, Risk, and Quality Engineering at Fortune Brands Home & Security. That work covered privacy and security risk, global regulatory compliance, product recalls, and quality systems. Since 2015 she has led IT risk management and the Office of the CISO at Northwestern Mutual. There she built an enterprise framework for quantifying technology risk to guide infrastructure investment and risk treatment decisions. She has taught as adjunct faculty at Northwestern University’s Pritzker School of Law since 2018.
Mark Henke – VP, IT Security & CISO, EVERSANA
Mark Henke came to security through infrastructure. As network services and infrastructure manager at Alterra Healthcare, he moved the company’s data center overnight to a new headquarters and designed a VPN across more than 340 sites that saved $300,000 a year in communication costs. He spent more than 11 years managing IT security and compliance at Brookdale Senior Living, leading a team of seven and implementing an identity governance system covering more than 180,000 user IDs across 40 platforms. After nearly four years directing IT security and control management at ACL Laboratories, Henke joined EVERSANA in November 2018 as VP of IT Security and CISO. He is a member of ISSA’s Wisconsin chapter and FBI InfraGard, and holds a CISM.
From the Factory Floor to the Security Office
Milwaukee’s manufacturing heritage shows up in how these leaders think. Lewis ran IT for a crane maker before she secured a utility’s operational technology. Farrell managed SAP at Rockwell Automation before running security at a retailer and a tool company. Stucker spent 15 years at a film manufacturer between the Army and a career in health care identity. Brzycki brought a patent agent’s precision and a decade of product compliance to IT risk quantification, and Henke built health care networks before defending them. In a city that still makes things, its security leaders tend to treat risk as an engineering problem, measured, documented, and fixed.
Discover more CISOs securing their organizations:
- The Crescent City’s Cybersecurity Leaders to Watch
- The Holy City’s Cybersecurity Leaders to Watch
- The Magic City’s Cybersecurity Leaders to Watch
- Perth’s Cybersecurity Leaders to Watch
- At the Heart of Europe: Belgium’s CISOs to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.