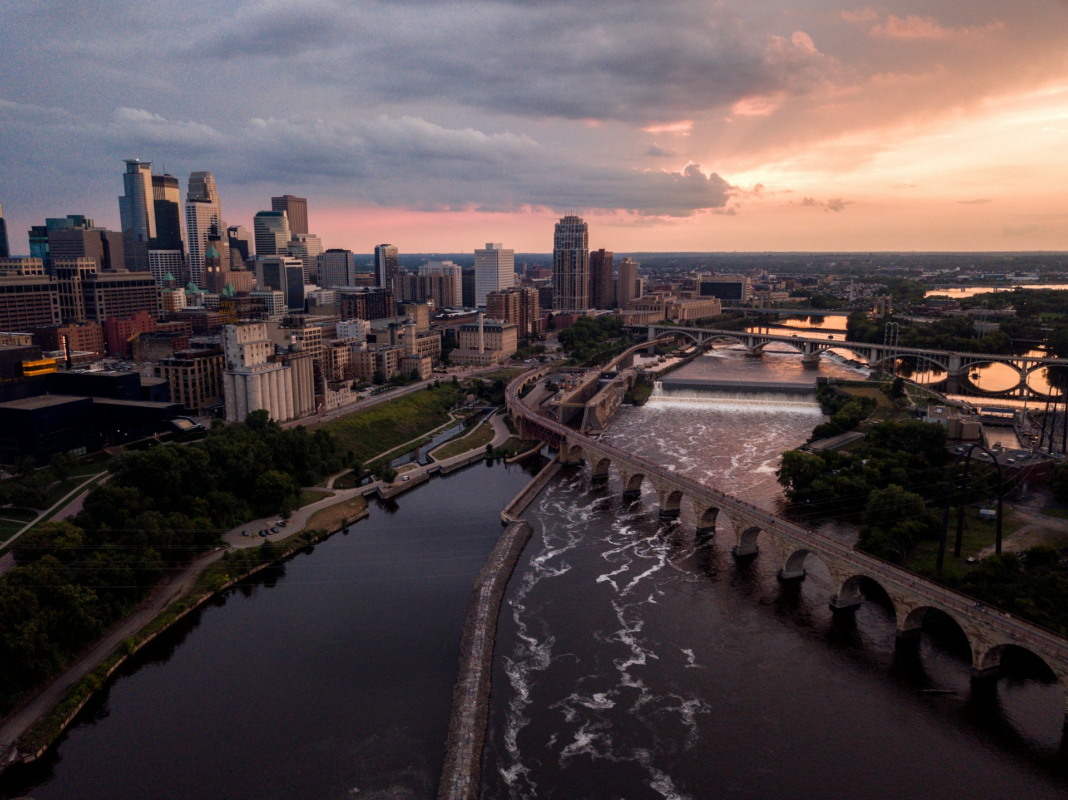
The Twin Cities economy runs on managed care, medical devices, and a state government that has professionalized its own security leadership as thoroughly as any private employer here. The seven leaders below secure a regional health plan, a medical device spinoff of 3M, the state of Minnesota itself, a hospital system, a medical equipment company, a building products manufacturer, and an educational testing firm. Several built their programs from a standing start inside the same organization over a decade or more, and two came up through business continuity before cybersecurity had its own department.
Brad Abbott – Senior Director of Information Security, CISO, Medica
Brad Abbott has spent eleven years at Medica, the Minnesota-based health plan, and has led its security organization as senior director and CISO since September 2020. He came up through risk and identity management, running IT risk, identity and access management, business continuity, and crisis management before the security title. Before Medica he spent eleven years at Target, leading large infrastructure programs including a $10 million cloud network build-out, a multi-year pharmacy application upgrade spanning thousands of in-store servers, and the technical selection and rollout of Oracle Identity Manager. His earliest security work was business continuity at Blue Cross and Blue Shield of Minnesota and Y2K and disaster recovery consulting at Ernst & Young, a career shape that runs from continuity planning into the security discipline it eventually became.
Kyle Erickson – VP, Product CISO, Solventum
Kyle Erickson became VP and Product CISO for 3M Health Care in November 2023 and continued in the role when the business spun off as the independent public company Solventum in April 2024. He leads global cybersecurity across product, cloud, manufacturing, and enterprise platforms for a large healthcare organization, with particular depth in medical devices and connected products. He came from Medtronic, where he spent nearly five years in product security, rising from director to senior director, and before that spent nearly eight years at Optum progressing from IT security consultant to director. He holds CISSP, HCISPP, and CCSP, and his focus across eighteen years has stayed consistent: embedding security into the full product lifecycle rather than bolting it on afterward.
John Israel – CISO, Minnesota IT Services
John Israel became Assistant Commissioner and CISO for the State of Minnesota in May 2023, after eight months in the role on an interim basis and more than two years before that as deputy CISO. His path is the most unusual on this list: fifteen years as a sheriff’s deputy for Washington County before joining state IT in 2008 as a forensic and SOC lead, then rising through security operations management and information security manager roles over a decade. Fifteen years in law enforcement followed by fifteen more in state cybersecurity is a career built entirely inside Minnesota public service, and it shows in how deliberately he moved through nearly every rung of the state’s security organization before reaching the top.
Ashok Kallam – CISO, Fairview Health Services
Ashok Kallam has spent more than eight years at Fairview Health Services and became its CISO in May 2024, after three and a half years as director of cybersecurity and associate CISO and two and a half as manager of identity management and access governance. His earlier career was entirely in consulting and managed services: twelve years at Wipro Technologies rising from technical lead to regional manager of enterprise security services, five years running infrastructure management and security for Happiest Minds Technologies across North America, and a stint as senior director of identity access management and PKI at SUPERVALU. That consulting background, built largely around one retail client relationship over a decade, gave him deep identity and access management expertise before he moved to the health system side. He joined the MinnesotaCISO board of advisors in 2025.
Greg Matthias – VP, CISO, Agiliti
Greg Matthias has been VP and CISO of Agiliti, the medical equipment management company, since August 2021. He came from TCF Bank, where he was EVP and CISO, and before that spent eight and a half years at the Defense Information Systems Agency as technical director and chief engineer, overseeing a $260 million annual portfolio of joint command and control, logistics, and information-sharing systems for the Department of Defense. His earlier career included four years at MITRE supporting US Strategic Command and DISA, and chief engineer roles on the DoD’s global command and control system of record. Few Twin Cities CISOs carry that density of defense engineering experience before entering the private sector, and it is a background built for a company whose equipment supports hospital operations nationwide.
John Strasser – Senior Director of Information Security and IT Compliance, Apogee Enterprises
John Strasser became senior director of information security and IT compliance at Apogee Enterprises, the building products manufacturer, in December 2023. He spent the prior decade at Sovos, the tax compliance software company, rising from information security manager through director to Chief Security Officer, a role reporting directly to the CEO. There he expanded ISO 27001 certification from a single system to 52 platforms across EMEA and Latin America, scaled remote work security through the pandemic, and led governance across a private equity portfolio of more than 26 entities. Before Sovos he built the information security function at Mattersight, formerly eLoyalty, and started as a network administrator at Corel. His entire security career, more than nineteen years, has run inside a handful of Twin Cities employers, each one building on the program he had already stood up at the last.
Aimee Martin – CISO, Data Recognition Corporation
Aimee Martin has been CISO of Data Recognition Corporation, the educational assessment and testing company, since December 2022. She came from Vista Outdoor, where she spent seven and a half years, rising from senior IT auditor to director of information security, compliance, and PMO, managing three teams and a $10 million budget, and leading IT divestiture of two international businesses worth roughly $150 million combined. Before that she built an IT audit function from scratch there, aligning it to COBIT. Her earlier career was pure audit: internal auditor roles at US Bank and Deloitte, and five IT security reviews for the Minnesota Office of the Legislative Auditor evaluating statewide project controls. That audit-first foundation, unusual among CISOs who come up through engineering, shows in her account of compliance work spanning SOX, GDPR, CCPA, ITAR/EAR, and HIPAA at once.
What This Group Says About the Twin Cities
The Twin Cities’ security bench is built on internal promotion more than lateral hiring. Abbott, Kallam, Israel, and Strasser all rose to the CISO seat inside organizations where they had already spent years in adjacent roles, business continuity, identity management, law enforcement, audit, rather than arriving from outside to take the title. That pattern produces security leaders with unusually deep institutional knowledge of the systems they protect, and it fits a regional economy anchored by long-tenured employers in healthcare, defense-adjacent manufacturing, and state government rather than by venture-backed software.
Discover more CISOs to watch:
-
- CISOs to Watch in Charlotte: From Theme Parks to Financial Services
- CISOs to Watch in LA: From Movie Studios to Storage Units
- CISOs to Watch in Austin: From the County Courthouse to the Cloud
- Houston’s Security Leaders to Watch: From the Refinery Floor to the Boardroom
- Boston’s CISOs to Watch: Securing Hospitals, Campuses, and Code
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.