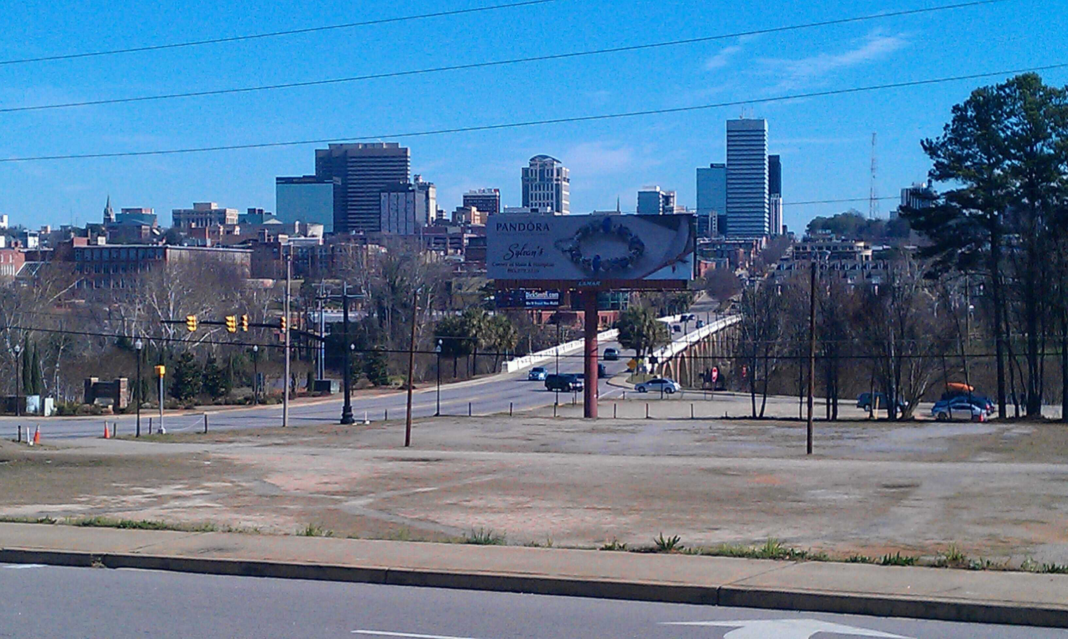
As South Carolina’s capital, Columbia concentrates its security leadership in state government, and four of the seven CISOs below protect state agencies covering public health, revenue, social services, and Medicaid. The others secure the state’s flagship university, a major law firm, and a federal healthcare contractor. Their paths into the role vary widely. One trained to maintain B-1 bomber avionics before becoming the Air Force squadron’s system administrator. Another started out processing Medicare claims. A third began as a computer repair technician and built a password-sharing app on the side.
Marcos Vieyra – Executive Director & CISO, University of South Carolina
Marcos Vieyra spent seven years in the U.S. Air Force, trained to support B-1 bomber offensive avionics but serving mostly as his squadron’s system administrator. He joined the University of South Carolina in 2001 as a network manager for the biology department, moved into the central security team running intrusion detection, and rose through information security officer and director of information security to CISO in 2012. In 2014 he became the first CISO of the State of South Carolina, leading the newly created Division of Information Security with oversight of more than 70 state agencies. After serving as CISO-in-Residence at the SANS Institute, Vieyra returned to USC in 2018 as Executive Director and CISO. He holds a long list of security and privacy certifications, including CISSP, GSTRT, CIPP/US, and CIPM, and was part of the inaugural class of IAPP Fellows of Information Privacy.
Brian Bannister – CISO, South Carolina Department of Public Health
Brian Bannister has served as CISO of the South Carolina Department of Public Health since February 2013, more than 13 years in the role. His experience spans information security, physical security, IT infrastructure management, and computer forensics. He also co-founded Compliance Innovations in 2006. He holds a bachelor’s degree in computer science with a minor in business administration from Lander University.
Will Boling – CISO, Maynard Nexsen
Will Boling started as a computer repair technician in Columbia and worked as a senior residential networking technician at the University of South Carolina. He spent more than six years as a senior systems engineer at EarthLink Business, then worked as an infrastructure engineer at EDENS. Along the way he freelanced as a web designer and developer and built SharePass, an application that lets users share passwords securely with IT staff. Boling joined Nexsen Pruet, now Maynard Nexsen, in 2015 as a senior engineer and rose through information security manager and director of information security to CISO in March 2024.
Sonya Ridgill – AVP & CISO, Companion Data Services
Sonya Ridgill has spent 29 years across BlueCross BlueShield of South Carolina and Companion Data Services, building her career in application development and enterprise modernization. She managed application development at BlueCross BlueShield of South Carolina for nearly 13 years and served as director of application development for more than seven. In August 2026 she became AVP and CISO of Companion Data Services, leading cybersecurity strategy, governance, compliance, and security operations in a federal healthcare environment. She holds a degree in computer science and mathematics from Charleston Southern University.
John Davis – CISO, South Carolina Department of Revenue
John Davis started as a programmer at Milliken Research in 1988 and spent five years as an engineering project manager at SC DHEC. He went on to run IT for law firms and a medical services company, then directed IT operations and network services at AgFirst Farm Credit Bank, bringing its data center through a major flood with minimal downtime and leading a full data center migration ahead of schedule and under budget. He was named a VMware vExpert three years running and co-founded the Carolina Technology Conference, which grew to draw 800 attendees from 14 states. After serving as VP of IT and security at Providence Health and as IS division director and HIPAA security officer at MUSC, he became CISO of the South Carolina Department of Revenue in June 2024. He holds degrees in engineering and physics and CISSP, CISM, and CPHIMS certifications.
Chris Lawrimore – CISO, South Carolina Department of Social Services
Chris Lawrimore has more than three decades in IT. He directed information technology at Newberry College, worked as a senior analyst at Federated Systems Group, and managed IT at Brookgreen Gardens. He then spent nearly 11 years at Fiserv in Chapin as information security operations manager and lead for its Sentry cybersecurity practice, serving credit union and banking clients. After more than six years as a network defense technical advisor at Trend Micro, he became CISO of the South Carolina Department of Social Services in August 2024. He holds CISSP, CISM, CCNA, and MCSE certifications.
Velton L. Baldwin – CISO, South Carolina Department of Health and Human Services
Velton L. Baldwin started at Palmetto GBA processing Medicare claims, training new associates and flagging potential fraud before moving into systems analysis and then security auditing of Medicare systems. He worked as a junior IT analyst at SCANA, then as an information systems auditor and security analyst at BlueCross BlueShield of South Carolina, supporting Medicare and Tricare environments. He joined the South Carolina Department of Health and Human Services in 2015 as IT compliance manager, overseeing security engineers and NIST controls, and has served as CISO since February 2022. He holds ABCP, CISA, and Security+ certifications.
Built for Public Service
Columbia’s CISOs show how much of a capital city’s security rests with government and the institutions around it. Vieyra built South Carolina’s statewide security division from the ground up before returning to USC. Davis, Lawrimore, and Baldwin brought experience from banking, healthcare, and Medicare contracting into state agencies, and Bannister has protected public health data for more than a decade. Boling and Ridgill grew into the CISO role at organizations they have served for years. In a city where public service is the largest employer, these leaders keep the systems South Carolinians depend on running safely.
Discover more CISOs securing their organizations:
- The Duke City’s CISOs to Watch
- On the Silicon Prairie: Omaha’s Cybersecurity Leaders to Watch
- Red Stick Defenders: Baton Rouge’s Cybersecurity Leaders to Watch
- In the Shadow of Pikes Peak: Colorado Springs’ Cybersecurity Leaders to Watch
- The Bold City’s Cybersecurity Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.