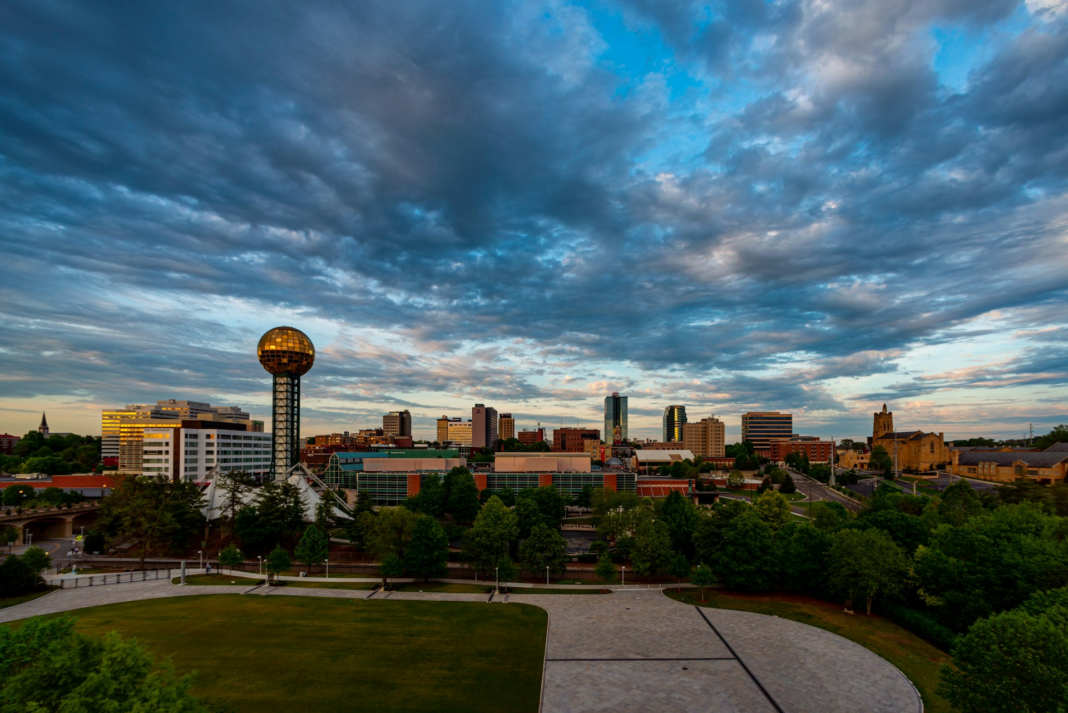
A former FBI cyber agent. A fire department captain who still works the mainframes. A security officer who built an entire IT operation from nothing for a startup medical device company. Knoxville’s cybersecurity bench pulls from federal law enforcement, hospital systems, higher education, and the compliance audit world, and several of these leaders have built or rebuilt security programs from scratch more than once.
Michael Murphy – VP & CISO, UT Medical Center
Michael Murphy has owned his own business, BMPTS, LLC, since 2001, running it alongside a security career that has now spanned 25 years. He spent more than eleven years at University Medical Center of Southern Nevada as Network Security Administrator and then Information Security Administrator, serving as technical lead for the information security team across firewalls, VPN, incident response, and HIPAA compliance. A brief stint as a Senior Network Security Engineer at Caesars Entertainment followed, then four and a half years at Structured Communication Systems consulting on PCI compliance as a QSA. Murphy returned to public sector work as an Information Security Administrator at Clark County and then at the City of Henderson, where he handled PCI DSS as an ISA. He rejoined University Medical Center of Southern Nevada in 2021, rising from IT Security Operations Supervisor to Information Security Officer and Director of Cyber Security. In November 2025 he became VP and CISO at UT Medical Center in Knoxville.
Rodger Paxton – Director of Cybersecurity, Covenant Health
Rodger Paxton built an entire IT and security operation from nothing for a brand-new medical device startup. At LV Liberty Vision he designed the cloud and on-premises infrastructure, deployed a zero-trust model through Azure Active Directory and Microsoft Endpoint Manager, and brought the company to full compliance with HIPAA, ISO 13485, and ISO 14971 while leading a fully remote team. His security awareness program lifted staff scores by 84%. Before that he spent nearly five years as IT and Network Manager and Security Officer at Strategic Behavioral Health in Memphis, where he led a 14-person team, stood up four new hospitals, and grew the network from two sites to ten. Paxton later served four years and ten months as Fractional CISO for the publicly traded life sciences company Aditxt, cutting cybersecurity spending by more than $750,000 through insourcing. As Director of Cybersecurity and Enterprise CISO at West Tennessee Healthcare, he covered nine hospitals, more than 90 clinics, and over 10,000 employees, reducing critical vulnerabilities by 60% and phishing susceptibility from 12% to 3%. He joined Covenant Health in Knoxville in July 2026.
Adam Keown – CISO, Eastman
Ten and a half years in the FBI shaped how Adam Keown approaches security leadership. He served as a Special Agent working cyber and counterintelligence in the Washington area, then led computer investigations, incident response, and forensics out of Louisville, testifying as an expert witness and coordinating threat intelligence sharing across industries. His career began as Director of Information Systems at North Georgia Electric Membership Corporation. After the FBI he spent two and a half years as Cybersecurity Practice Manager at TEKsystems, designing programs for finance, healthcare, retail, insurance, and government clients. Keown then spent three years in the Knoxville metro area as Cybersecurity Risk Program Manager at the Tennessee Valley Authority, translating security threats into business terms for stakeholders across the utility’s operating environments. He became CISO of Eastman in September 2019, where he now oversees three cybersecurity teams covering corporate systems, manufacturing sites, and 14,000 employees globally. He is also a distance runner, a discipline he connects directly to the patience executive leadership requires.
Brandon Thompson – CISO, A-LIGN
Brandon Thompson taught security classes as a certified AlienVault instructor, consulting for organizations including Nasdaq and the UK Ministry of Defence. He started as a Systems Administrator at Park West in Knoxville, spending seven years managing information security, network and server infrastructure, disaster recovery, and IT policy while overseeing the company’s intern program. After a year at Claris Networks he joined Sword & Shield Enterprise Security, where he worked as a Systems Engineer and then Solutions Architect, serving as virtual CISO for multiple enterprise clients and running risk assessments under NIST SP 800-30 for healthcare, financial, manufacturing, and retail organizations. Thompson joined A-LIGN in 2016 as a Senior Consultant and has been promoted five times since, through Managing Consultant, Senior Manager for PCI, Director of ISO and HITRUST, and Senior Director of Cybersecurity and Compliance Services. He became CISO in January 2024. He holds CISSP, CISM, CISA, PCI QSA, and HITRUST CCSFP certifications alongside a bachelor’s degree in IT security.
Richard Heatherly – Cyber Security Manager/CISO, 21st Mortgage Corporation
For nearly eleven years, Richard Heatherly served as a captain and board member at the Paulette Fire Department in Maynardville, managing 25 employees, budget planning, and fire ground operations. He has spent his entire technology career at 21st Mortgage Corporation, joining in February 2004 as an Operations Administrator. In that role he still maintains daily operations across four system partitions on AS400 and IBM i systems, administers disaster recovery solutions, and handles backup administration. Heatherly added the Cyber Security Manager and CISO title in April 2014. He built the company’s information security program and strategy from the ground up, established its corporate risk self-assessment methodology, and created the computer incident response plan and team, including annual tabletop exercises with auditable findings. He delivers monthly security updates to the board.
Matt Williams – CISTO, University of Tennessee System
Eight years in the US Army started Matt Williams on his path, first as a Senior EWS Operator for more than five years and then as an IT Specialist. He moved into higher education at Bucknell University, working as a network administrator and then Assistant Director of Networking. Four years at Kent State University followed, where he served as Lead Security Engineer and managed network and telecommunications services. He joined The University of Akron in 2019 as Director of IT Infrastructure Services, became CISO in 2021, and later added Associate CIO responsibilities. Williams moved to the University of Tennessee, Knoxville in February 2024 as Associate CIO and CISO, then became Assistant Vice Chancellor and Chief Information Security and Technology Officer that July. He was named CISTO for the University of Tennessee System in January 2025.
Programs Built From Nothing
What connects this group is how often each has started with a blank page. Paxton built a complete IT and security operation for a startup medical device company, then did it again at a nine-hospital health system. Heatherly wrote 21st Mortgage’s first information security program, its risk assessment methodology, and its incident response plan while continuing to run the company’s mainframe operations. Thompson served as virtual CISO for multiple enterprise clients before building A-LIGN’s own security function. Murphy has stood up security programs at a county government, a city, and two hospital systems in two states. Keown brought FBI investigative discipline to a Fortune 500 manufacturer, and Williams has led security at three universities across three states. In Knoxville, the common qualification is not a particular credential but a track record of building something where nothing existed.
Discover more CISOs securing their organizations:
- Buffalo’s Cybersecurity Leaders to Watch
- Cleveland’s Cybersecurity Leadership Bench
- Orlando’s Cybersecurity Leadership Bench
- Where Two Rivers Meet: Sacramento’s Cybersecurity Leaders to Watch
- Derby City’s Cybersecurity Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.