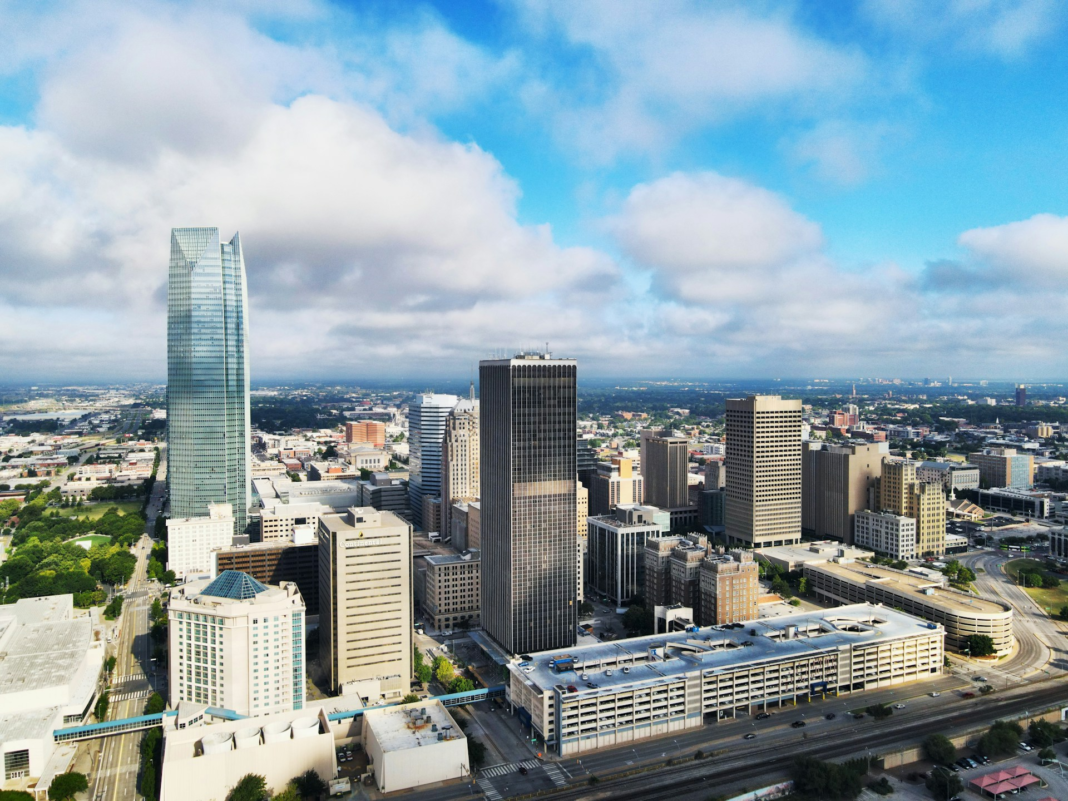
The cybersecurity bench in Oklahoma City is built around a handful of very large local employers: two health systems, a national craft retailer, a travel stop chain, and a university medical center. Several of the people below have spent a decade or more at the same organization. Two of them started their careers examining banks. One was working at the Federal Reserve Bank of Kansas City’s Oklahoma City branch on the morning of April 19, 1995.
Stacy Stika – VP & CISO, INTEGRIS Health
Stacy Stika began her healthcare career as a medical assistant and urgent care office manager. She spent three years in that role at John Muir Health in Walnut Creek, California, then moved into health information management as an Epic analyst in 2012. Stika became an Epic Security Analyst in 2014 and worked her way through lead analyst and manager roles covering identity and access management and technical risk. Optum brought her in to direct information security supporting John Muir Health, and in July 2021 she became the health system’s CISO. She joined INTEGRIS Health, the largest health system in Oklahoma, as VP and CISO in September 2022, where she leads strategic planning, implementation, and governance for information security and technology services. She holds the HCISPP credential from ISC2.
Kent Nabors – AVP & CISO, Hobby Lobby
Kent Nabors was on site at the Federal Reserve Bank of Kansas City’s Oklahoma City operations during the 1995 bombing, part of the team that kept the Fed running through the lockdown that followed. He calls it an early, firsthand lesson in disaster recovery and incident response. His career had started in bank examination, first with the FDIC in Austin during the cleanup from the late-1980s banking crisis, then at the Federal Reserve, where he moved from financial analysis into network administration. Nabors joined MidFirst Bank in 1998 and stayed more than 18 years, progressing from network administrator to VP and Director of Information Security and then becoming the bank’s first CISO in 2012. That role included physical security across more than 80 banking centers and 100 properties nationwide. He has served as AVP and CISO of Hobby Lobby since August 2016, leading enterprise cybersecurity, privacy, and PCI compliance while sitting on the company’s AI governance committee. Nabors argues that security is a property of a system rather than a function within it. A ship, as he puts it, does not have a buoyancy department. He has contributed to several books, runs a small business with his wife, and spends time in his woodworking shop.
Monte Coulter – VP & CISO, OU Health
Monte Coulter spent 15 years at GAF, the roofing manufacturer, rising from senior network administrator to Director of Cybersecurity and CISO. In that role he built the company’s entire information security policy framework, introduced SIEM, multi-factor authentication, network segmentation, and penetration testing, and grew the team from two people to thirteen on a $5 million budget. He also served as the company’s focal point for security and compliance during a worldwide migration from Microsoft Office to Google Workspace covering 15,000 users across 80 countries. Coulter then spent nearly two years as Senior Director of Information Security and CISO at Caris Life Sciences in the Dallas-Fort Worth area. He joined OU Health in January 2023 and became Vice President and CISO two months later. He previously served on the Cybersecurity Advisory Board at Rutgers University.
April Dickson – Director of Information Security, University of Oklahoma Health Sciences Center
April Dickson started out as a trainer and customer service representative at a software company before moving into technology support. She spent nearly six years at Chickasaw Nation Industries, advancing from computer technician to server administrator team lead and then Systems Security Officer, where her work covered FISMA compliance and system security planning. Brief stints as a security analyst at Chesapeake Energy and an infrastructure administrator at Coppermark Bank followed. Dickson joined the University of Oklahoma Health Sciences Center in 2013 as an IT Security Architect and became Director of Information Security in January 2019. She now oversees governance, risk, and compliance staff, leads forensic and incident response processes, and manages IT continuity of operations and disaster recovery planning. Her compliance work spans NIST 800-171, PCI DSS, GLBA, and the NIST Cybersecurity Framework. She holds CISSP certification.
Paul Baresel – Director of IT Security (CISO Equivalent), Love’s Travel Stops
Oil and gas is where Paul Baresel built his foundation. He spent eight and a half years as a senior security analyst at Chesapeake Energy, then moved to Farmers Insurance as Cyber Defense Manager before returning to the energy sector as Director of IT and Security at American Energy Partners. He joined Paycom in 2016, spending seven years there and eventually serving as Director of IT Security. Baresel became Director of IT Security at Love’s Travel Stops in October 2023. Across his career he has scaled security teams from eight people to organizations of more than 100, built security operations centers, and implemented governance frameworks including ISO 27001, PCI DSS, and SOC 2 for companies in oil and gas, fintech, retail, e-commerce, and SaaS.
Built on Oklahoma City’s Largest Employers
What this group shares is depth in a small number of very large organizations. Stika and Coulter run security for the state’s two biggest health systems, and Dickson protects the university medical center that trains much of their clinical workforce. Nabors spent 18 years at MidFirst Bank before Hobby Lobby, and Baresel came up through Chesapeake Energy and Paycom, two of the city’s most prominent employers. Four of the five hold their current roles after a decade or more in Oklahoma City, and three came into security from somewhere else entirely: bank examination, urgent care administration, and customer service training. In a metro this size, that kind of local continuity means the people defending these institutions tend to understand them from the inside out.
Discover more CISOs securing their organizations:
- From the Tennessee Valley: Knoxville’s Cybersecurity Leaders to Watch
- Buffalo’s Cybersecurity Leaders to Watch
- Cleveland’s Cybersecurity Leadership Bench
- Orlando’s Cybersecurity Leadership Bench
- Where Two Rivers Meet: Sacramento’s Cybersecurity Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.