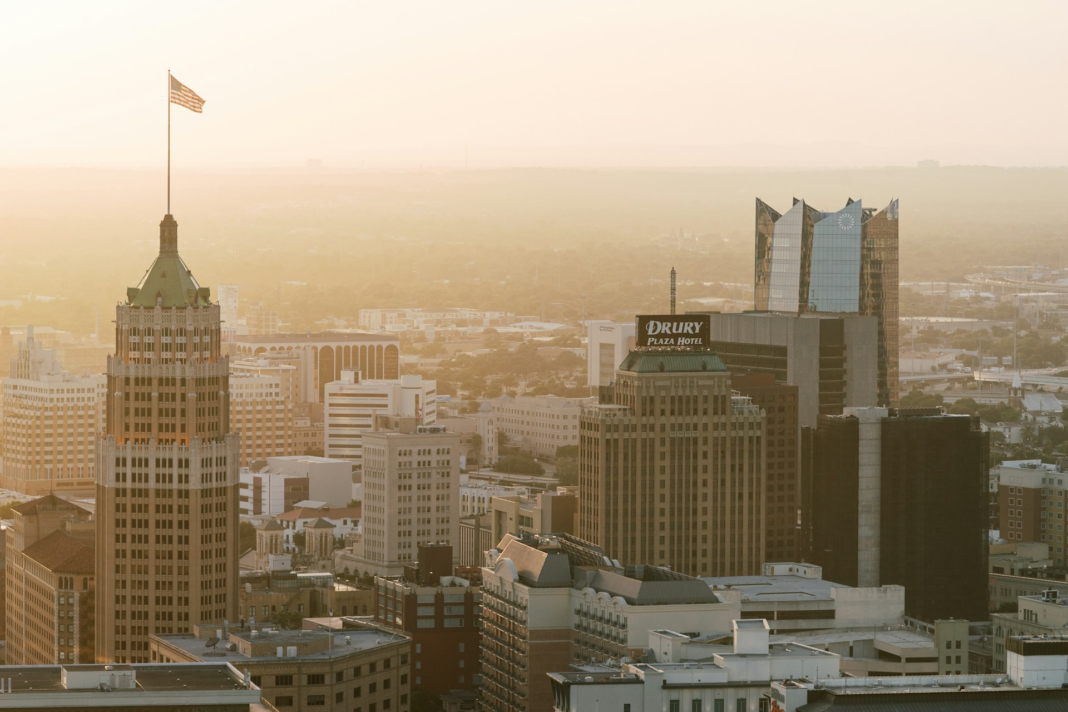
San Antonio carries the nickname Military City USA, and three of the four leaders below earned it for their town. Between them they have served in the Air Force, the Navy, the National Security Agency, and the Cybersecurity and Infrastructure Security Agency. The fourth came up through manufacturing floors and Lean Six Sigma before running security for a global marketplace. Today they protect a municipal utility, the city government and its regional security operations center, a financial services firm, and a cloud and AI services company.
Paul J. Guerra – CISO, Rackspace Technology
Paul J. Guerra started in manufacturing. He managed a production line of more than 80 people building custom servers for Hewlett Packard, then ran the launch of a $50 million manufacturing site for Toyoda Gosei, a Toyota supplier. At USAA he used Lean Six Sigma to standardize claims workflows and streamline annuity fulfillment. He brought that operational discipline to Rackspace in 2011 as Director of Security Operational Excellence. From there he led security strategy and operations for the Yahoo team known as the Paranoids, then served as Chief Security Officer and CISO at Argo Group. At StockX he built an Enterprise Trust organization of 150 people spanning security, fraud, market integrity, IT, and platform engineering. His team developed a fraud model using 250 risk signals to flag high-risk transactions before physical authentication. In February 2026 Guerra returned to Rackspace as CISO, leading roughly 100 people across security operations, engineering, GRC, and fraud.
Jonathan Homer – CSO & VP, Integrated Security, CPS Energy
Critical infrastructure incident response is where Jonathan Homer built his career. He spent nearly a decade at Idaho National Laboratory supporting the Department of Homeland Security’s ICS-CERT, coordinating isolation, eradication, and forensics after cyberattacks on U.S. industrial control systems. He also ran the lab’s cybersecurity training and awareness program for the Department of Energy. Homer moved to CISA in 2017 as chief of the Industrial Control Systems Group within its hunt and incident response team, then served as Branch Chief for Threat Hunting. In March 2022 he joined CPS Energy, San Antonio’s municipal utility, as Chief Security Officer and Vice President of Integrated Security. Before all of it, he ran his own business, Centrisys Communications.
Shannon Lawson – CSO & Director, Alamo Regional SOC, City of San Antonio
Shannon Lawson led offensive cyber operations for the NSA’s Red Team, targeting the Joint Staff, unified commands, and federal agencies to test their defenses. That followed four years as a Navy cryptologic communications technician. He handled incident response for the Navy-Marine Corps Intranet at Raytheon, then built an information assurance program from scratch at the Naval Information Warfare Center Pacific, training more than 1,200 personnel. After three years as CISO for NAVWAR, he became CISO and CTO for the State of Alaska, unifying security across 15 agencies and growing its security operations team from 6 to 35. NASCIO recognized his work there with the 2018 Thomas M. Jarrett Cybersecurity Scholarship. As Assistant CIO, CISO, and Chief Privacy Officer for the City of Phoenix, he oversaw security for 80,000 endpoints and led recovery of all citywide functions within 10 hours after a major system failure. Lawson joined the City of San Antonio in November 2025 as Chief Security Officer and Director of the Alamo Regional Security Operations Center.
Jeffrey Julig – CSO, SVP & CISO, SWBC
Jeffrey Julig spent 25 years in the Air Force. He began in nuclear security, then provided protection for personnel and aircraft in Kenya and Somalia during Operation Restore Hope. He supported continuity operations at the Pentagon during and after the September 11 attacks. Later he served in an inaugural senior position in the Air Force’s first Cyber Command and deployed in support of Special Operations Forces in Iraq. Julig joined SWBC in January 2016, where he leads a converged program covering information security, privacy, physical security, and resilience. He chairs the company’s Security Risk Committee and sits on its advisory board. His programs have produced seven annual AICPA audit reports and two PCI DSS Level 1 assessments. They also support more than 1,000 due diligence reviews each year from banks and regulators.
Where the Mission Came From
Three of these four learned security on missions that could not be allowed to fail. Julig guarded nuclear assets and helped stand up Air Force Cyber Command. Lawson ran red team operations for the NSA before leading security for a state and two cities. Homer hunted intruders inside the nation’s industrial control systems for DHS and CISA. Guerra took a different path, applying the process discipline of manufacturing and Lean Six Sigma to security programs at a marketplace, an insurer, and now a cloud company. What they share is a habit of treating security as operations rather than paperwork. In a city built around military installations, that habit fits.
Discover more CISOs securing their organizations:
- The Flower City’s CISOs to Watch
- The Sun City’s Cybersecurity Leaders to Watch
- Between the Lakes: Madison’s Cybersecurity Leaders to Watch
- The House Always Defends: Las Vegas’s Cybersecurity Leaders to Watch
- Victoria’s Cybersecurity Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.