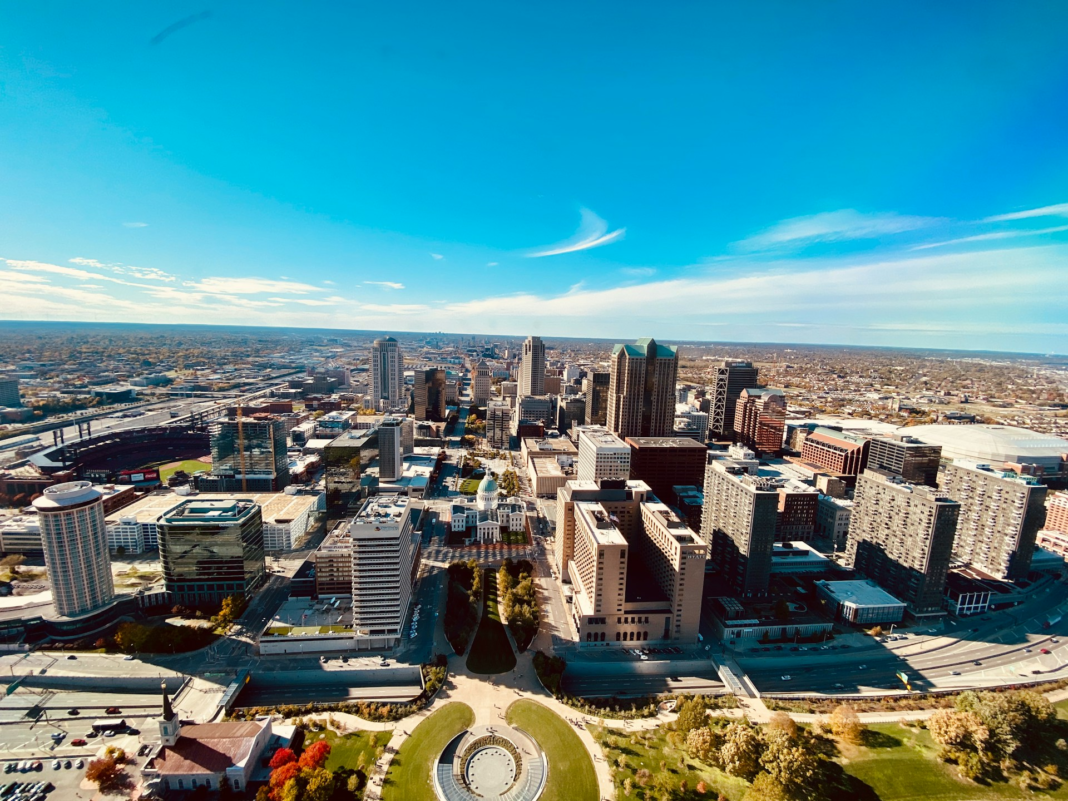
St. Louis’s security leadership bench spans a former NSA technical director turned technology consulting CISO, a grocery chain executive who built an enterprise security office from a single named role in 2014, and a Federal Reserve Bank veteran who moved from central banking into healthcare security this year. Technology, energy, retail, industrial manufacturing, healthcare, and consumer products all draw from the same regional talent pool, and the paths into these seats are as varied as the industries themselves.
Mike McGlynn – CISO, World Wide Technology
Mike McGlynn spent more than 25 years in federal government service before joining the private sector, rising to the Senior Executive Service as a technical director in software development, systems design, and cryptomathematics. McGlynn’s government career earned him the Presidential Rank Award for Meritorious Executive Service, two Meritorious Civilian Service Awards, and the Deckert-Foster Excellence in SIGINT Engineering Award. He joined World Wide Technology in 2010 and founded the company’s security consulting business, helping grow WWT’s security division from an early-stage startup into a business generating more than $2 billion in revenue by 2022. McGlynn became WWT’s Global Chief Information Security Officer in January 2024, leading a team of senior security experts, architects, and engineers who protect the company’s business assets. He has also served as a board director for HyperQube, a cloud-based virtual infrastructure orchestration company, and for CyFir, a distributed digital forensics firm acquired by eSentire in 2021. McGlynn holds an M.S. in Computer Science from Johns Hopkins University and a B.S. in Mathematics from the State University of New York at Albany.
Ryan Gibbs – VP & CISO, Ameren
Ryan Gibbs started his career at Best Buy’s Geek Squad before moving into enterprise IT and, eventually, utility-sector cybersecurity leadership. Gibbs spent eight years at PwC in Greater St. Louis, leading audit and consulting teams across attestation services, integrated IT audits, fraud risk assessments, and cyber risk assessments for clients in multiple industries. He joined Ameren in 2018 as Senior Director of GRC and Cybersecurity, then became Deputy CISO in June 2023, where he led cybersecurity risk management, data privacy, third-party risk, threat management, and vulnerability management programs. Gibbs was promoted to Vice President and CISO in March 2025. Ameren is a Fortune 500 company and the parent of Ameren Missouri and Ameren Illinois, serving 2.4 million electric customers and more than 900,000 natural gas customers across a 64,000-square-mile territory, with Ameren Missouri ranking as the state’s largest electric power provider.
Joey Smith – Enterprise CISO & VP, Schnuck Markets
Joey Smith spent four years investigating fraud for MasterCard’s global incident response team before Schnuck Markets named him its first-ever CISO in January 2014. Smith built the company’s Security Operations, Threat and Vulnerability Management, and Governance Risk and Compliance teams from the ground up, implementing a risk-based security strategy that has continued to expand his responsibilities ever since. His role grew to include Cloud Strategy, Network Engineering, IT Infrastructure, Disaster Recovery, Telephony, and IT Help Desk oversight, and in 2025 he was tasked with creating and leading the Schnucks Enterprise Information Security Office, which now supports the company’s full portfolio of family-owned businesses, including Desco, NAI Desco, and the Family Office. Before Schnucks, Smith worked MasterCard’s Account Data Compromise team, coordinating fraud alerts with merchants, issuers, and card brands, and served on the PCI Security Standards Council reviewing the work of PCI forensic investigation firms. He holds CISSP and EnCE certifications, the latter earned during an earlier career in computer forensics and data recovery. The Security Advisor Alliance named him a Rising Star in 2015, and Southeast Missouri State University recognized him with its Young Alumni Merit Award in 2014, the same year he led the university’s first Cyber Security graduates into their commencement ceremony. Smith also advises and mentors startups through SixThirty CYBER, a St. Louis venture program backed by regional CISOs and Cultivation Capital.
Scott Kampwerth – VP & CISO, Emerson
Scott Kampwerth has spent nearly two decades at Emerson, building his security career from the ground up after starting as a network engineer at two Missouri-based companies in the 1990s. Kampwerth joined Emerson in 2007 and spent more than 11 years as Director of Security Operations before becoming Deputy CISO in November 2018. He was promoted to Vice President and Chief Information Security Officer in May 2023, a role now in its fourth year. Before Emerson, Kampwerth worked as a Senior Network Engineer at GMAC Insurance and, earlier still, as a Network Engineer at Xyquad, Inc., experience that grounded his security leadership in hands-on network infrastructure work rather than a purely governance-focused track.
Jeff Zove – VP of Information Security, Mercy
Jeff Zove spent more than 18 years at the Federal Reserve Bank of St. Louis before moving into healthcare security this year. Zove served as the Fed’s Information Security Officer starting in 2019, overseeing the St. Louis District’s cyber security program while also serving as the bank’s Data Privacy Officer and coordinating its Insider Risk Management Team. His responsibilities there spanned policy, risk, compliance, vulnerability management, incident response, and security architecture. Zove was promoted to Vice President in 2022, continuing in the Information Security Officer capacity until his departure. He joined Mercy as Vice President of Information Security in July 2026. Earlier in his career, Zove worked as a Performance Outcomes Manager at Big Brothers Big Sisters of Eastern Missouri, a nonprofit background distinct from the banking and technology roles that would define the rest of his career.
Michael Evans – Head of Information Security, Energizer Holdings
Michael Evans built his security career on a foundation of software engineering, starting at Cerner Corporation in Kansas City before moving through a series of architecture and consulting roles across the Midwest. Evans’s most distinctive stretch came as a self-employed consultant, where he spent two years as Senior Cloud Architect Consultant for the Mayo Clinic, helping the research institution’s teams harness Google Cloud Platform’s genomics and big data capabilities while building disaster recovery and business continuity policies. He also consulted on a USPS kiosk development project for Hewlett Packard Enterprise, working alongside Escher and IBM on agent systems coding. Evans spent nearly five years as Senior Information Security at Principal Financial Group starting in 2019, specializing in attribute-level encryption and ensuring compliance with FINRA, HIPAA, and supply chain management standards while serving as an enterprise security subject matter expert. He also held the Head of Information Security title at Envestnet during part of that same period. Evans became Head of Information Security at Energizer Holdings in March 2024, where he now leads data classification frameworks, third-party risk management programs, and secure practices for the company’s artificial intelligence initiatives, aligning the organization’s security strategy with the NIST Cybersecurity Framework.
A Region Built on Career Pivots
What sets St. Louis apart is how many of these leaders arrived from somewhere else entirely. McGlynn spent a quarter century in federal cryptomathematics before ever setting foot in the private sector. Smith investigated payment card fraud for MasterCard before Schnucks handed him a named CISO title that didn’t yet have a template to follow. Zove spent nearly two decades inside a central bank before healthcare recruited him this year, and Evans built his security instincts through software engineering and cloud architecture consulting rather than a traditional security track. Only Gibbs and Kampwerth followed anything resembling a conventional internal climb, and even they built their foundations in audit and network engineering before security became the title on the door. St. Louis’s security leadership looks less like a pipeline and more like a landing spot for people who built serious expertise doing something else first.
Discover more CISOs securing their organizations:
- Securing Music City: Nashville’s Cyber Leaders to Watch
- Guarding the Gateway: Security Leaders to Watch in Miami
- Securing the Motor City: Detroit’s Security Leaders to Watch
- Desert Defenders: CISOs to Watch in Phoenix
- Guarding the Triangle: Information Security Leaders to Watch in Raleigh-Durham
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.