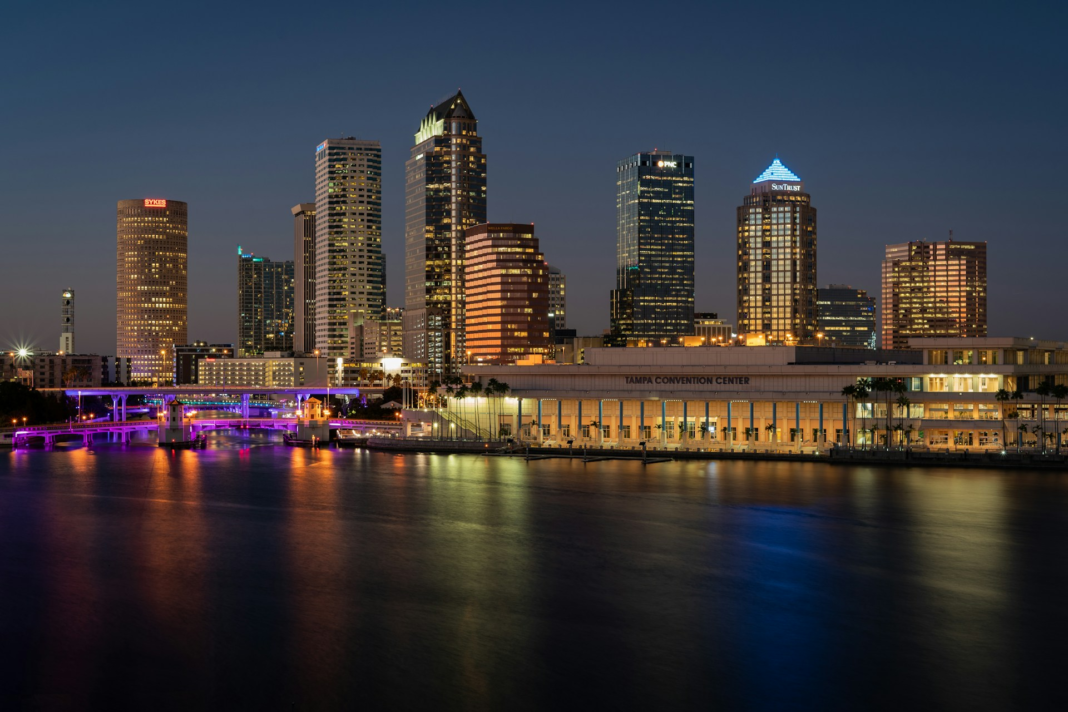
Tampa Bay’s CISO roster includes a former Marine Corps sergeant, a combatant command veteran who once led a 45-person joint cyber center defending military networks across US Central Command, and a security leader who has held the same title at the same city government since 1998. Financial services, healthcare, government, and cybersecurity vendors all draw from the same regional bench, and the five profiles below show just how differently each person got there.
Todd Ferguson – CISO, Raymond James Financial
Todd Ferguson spent nine years as a Marine Corps sergeant before starting a systems engineering career that eventually put him in charge of security for one of the country’s largest financial services firms. Ferguson joined what would become Raymond James as a Systems Engineer in 1997, then moved into a senior network engineer role in 2000 before transitioning into information security in 2005. He spent six years as Manager of Information Security starting in 2007, then advanced to Vice President of Information Security and Network Infrastructure in 2014. Ferguson took on the CISO title for Raymond James Bank and Raymond James Trust in 2019, first as deputy and then in the top security seat, before becoming CISO for the full Raymond James organization in October 2021, a role based in the Greater Tampa Bay Area that he has now held for five years. He also served as a founding board member of the Fuel User Group.
Martin Zinaich – CISO, City of Tampa
Nearly three decades before most cybersecurity job titles existed, Martin Zinaich built the City of Tampa’s first Information Security Office. He has held the CISO title there since 1998, a tenure that spans enterprise directory services implementations, DirXML and LDAP deployments, and the buildout of the city’s certificate authority and firewall infrastructure. Zinaich also served on the management team that implemented ITIL practices for Tampa’s Technology and Innovation department, and his work has included preparing RFPs for major infrastructure build-outs alongside ongoing compliance monitoring against federal regulations and industry standards. Earlier in his career, he worked as a Senior Application Programmer Analyst and, before that, as a Research and Development Engineer at Teleprompter, where he designed cable television equipment down to the component level, including circuit design and PC board layout.
Brian Jack – CISO & Founding Engineer, KnowBe4
Brian Jack has held the title of Founding Engineer alongside Chief Information Security Officer at KnowBe4 since September 2010, a dual role that has run for more than 16 years as the company grew into a major security awareness training provider based in Clearwater. Jack’s work there has spanned compliance management, API and web development, anti-fraud engineering, and penetration testing. Before KnowBe4, he worked as a Lead Security Analyst at GFI Software, where he led research and development for the CWSandbox and GFISandbox malware analysis platforms while also working as a Python and PHP developer. He spent time earlier as a Software Engineer at Raytheon, leading security design and integration tasks for a Department of Defense research and prototyping team, and as an Associate in PricewaterhouseCoopers’ federal security practice, where his audit and compliance clients included the Centers for Medicare and Medicaid Services, the CDC, and the Social Security Administration.
Doug Fee – CISO, Moffitt Cancer Center
For 15 years, Doug Fee served as CISO of University of Kentucky HealthCare, sitting on the CIO’s executive team with accountability for the privacy, confidentiality, and integrity of the health system’s information assets. Fee moved into that role in May 2009 after working as a Senior IT Risk Analyst at Fifth Third Bank and a Senior IT Infrastructure Engineer at RJ Corman Railroad Group. He became CISO of Moffitt Cancer Center in Tampa in May 2024, bringing more than two decades of healthcare-specific security leadership to one of the country’s leading cancer research and treatment centers.
John Burger – CISO & VP of Infrastructure, ReliaQuest
Before John Burger led cybersecurity for a private company, he led it for one of the US military’s combatant commands. Burger served as Chief of the Cyber Security Division, effectively CISO, for US Central Command starting in 2011, leading a joint staff of 72 people responsible for cyber defense policy and computer network defense operations. Under his leadership, the command scored outstanding on its Command Cyber Readiness Inspection, the first four-star combatant command headquarters to do so, while reducing its highest-risk vulnerabilities by more than 80%. He went on to lead CENTCOM’s Joint Cyber Center, directing a staff of 45 through full-spectrum cyberspace operations and developing a risk-scoring methodology that was later adopted as the foundation for a cyber security cooperation program with Gulf partner nations. After three years running his own firm, Cyber Security Insights, Burger joined ReliaQuest in 2017 as Vice President of Threat Management, then became CISO and Vice President of Infrastructure in October 2018, a role based in Tampa that he has now held for eight years.
Military Roots Run Deep in Tampa’s Security Bench
What stands out across this group is how many built their security instincts somewhere other than a corporate office. Ferguson spent nine years as a Marine Corps sergeant before ever touching a network engineering role. Burger ran cyber operations for an entire combatant command before bringing that discipline to the private sector. Zinaich has outlasted nearly every technology trend of the last three decades by staying in one government role since before most people considered cybersecurity a distinct profession. Tampa Bay’s CISO bench draws on federal, military, and public-sector experience in a way that few regional rosters can match, and it shows in how these five talk about risk.
Discover more CISOs securing their organizations:
- Guarding the Gateway: St. Louis’s Security Leaders to Watch
- Securing Music City: Nashville’s Cyber Leaders to Watch
- Guarding the Gateway: Security Leaders to Watch in Miami
- Securing the Motor City: Detroit’s Security Leaders to Watch
- Desert Defenders: CISOs to Watch in Phoenix
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.