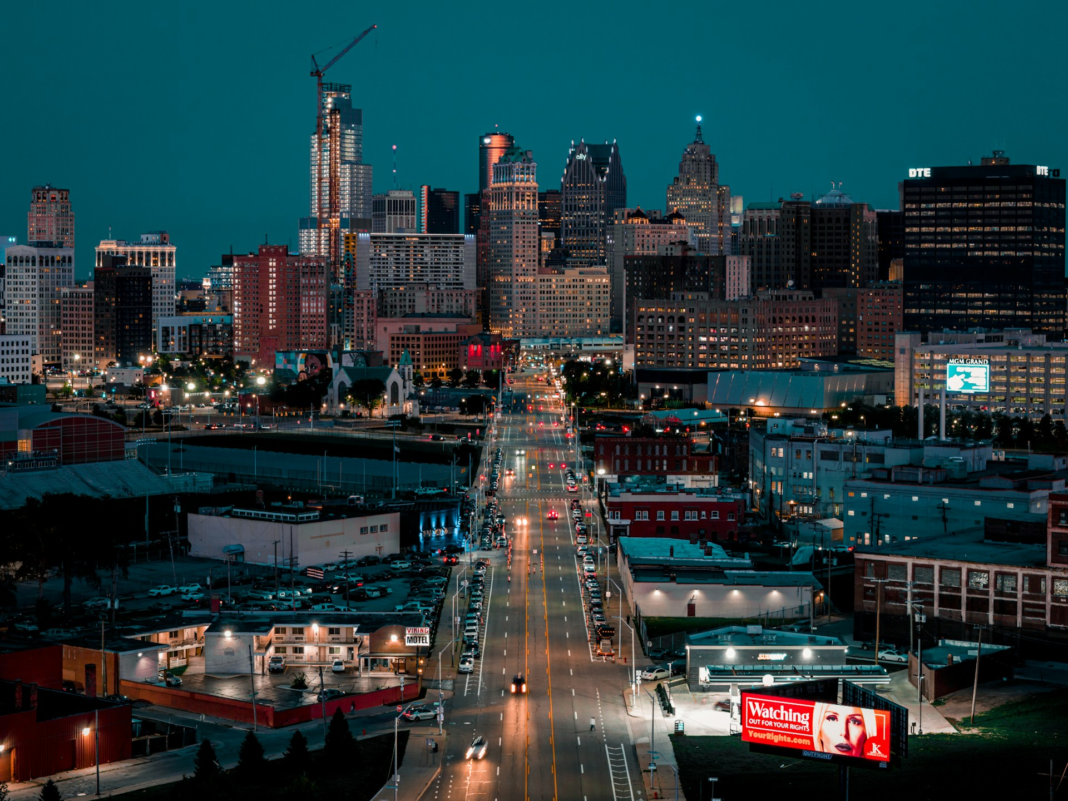
Detroit’s security leadership roster includes a former Navy torpedo technician, an Army combat engineer who started in a help desk job, and an executive who briefly ran two C-suite functions at once. It also includes someone who built a seven-year cybersecurity career at General Motors only to move into a completely different executive lane. The common thread across this group isn’t a shared background. It’s what each person did with an unlikely starting point.
Brent Cieszynski – VP & CISO, Blue Cross Blue Shield of Michigan
Brent Cieszynski spent his first working years installing digital printing equipment for Xerox in Southfield, Michigan, a job that predates his security career by more than a decade. He moved through IT and project management roles before joining Deloitte & Touche in 2005, where he managed SAP and Oracle security and control implementations for enterprise clients. At GE starting in 2010, he led a global team responsible for cyber security solutions across more than 350,000 endpoints, covering antivirus, host intrusion detection, and endpoint encryption. He moved into GE Aviation’s cyber security leadership in 2014, then took the Vice President role for Digital Technology Security & Compliance at GE Digital in 2017, protecting roughly 350,000 employees across more than 150 global locations. Cieszynski has served as VP and CISO of Blue Cross Blue Shield of Michigan since June 2018, where his team covers governance, risk and compliance, threat management, cyber operations, security architecture, and identity management for the company, Blue Care Network, and affiliated subsidiaries.
Steve Herrin – Director, Cybersecurity Information Security Officer, Strategy, Risk and Engagement, DTE Energy
Steve Herrin’s path to cybersecurity leadership ran through twelve years in the US Navy’s Torpedo Division aboard fast attack and ballistic missile submarines, followed by a stretch selling multimillion-dollar energy insurance accounts before he joined the Department of Homeland Security in 2007. At DHS he worked energy sector physical and cyber security for eight years and co-chaired the Nuclear Sector Joint Cyber Security Sub-Council. He then managed NERC’s CRISP program, a public-private threat intelligence sharing platform, on an $8 million annual budget before becoming NERC’s Director of Operations and Strategic Partnerships in 2017, where he sat on the E-ISAC executive management team and oversaw a $30 million budget. After a nine-month stint as an independent consultant advising European and Eurasian utilities on cybersecurity posture, Herrin joined DTE Energy in May 2021. He now manages IT and operational technology cybersecurity programs across five business units with more than 100 direct and indirect reports and a $25 million budget, protecting systems serving 3.6 million electric and gas customers. Under his leadership, DTE raised its OT cybersecurity maturity scores by 25% within two years and established a Technology Cybersecurity Committee to give the board direct oversight of cyber risk.
Scott Sadlocha – SVP, CISO, United Wholesale Mortgage
Scott Sadlocha served three years as a Combat Engineer in the US Army’s Airborne divisions before starting a help desk job at LDM Technologies in 2000. He moved into systems administration at Tower International in 2004, then joined United Wholesale Mortgage as an IT Security Analyst in 2013. From there, Sadlocha rose through information security engineer and team lead roles before becoming VP and CISO in January 2018, a title he has held in an expanded SVP capacity since February 2022. He has also served as a member of Evanta’s Detroit CISO Governing Body since 2018, a role that has run in parallel with his rise at UWM for most of his tenure there.
Adam Keagle – CISO, Detroit Diesel Corporation
Adam Keagle led RSM US LLP’s regional payment security practice and its national FedRAMP 3PAO team during more than five years as a director in the firm’s Risk Consulting group, work that covered regulatory compliance reviews, security testing, and vulnerability assessments for middle-market clients. Before that directorship, he spent five years at RSM as a manager in security and privacy consulting, and before RSM he worked as a software security penetration tester at GE, assessing products from the company’s aviation, healthcare, transportation, energy, and finance business units. Keagle started his career at SAIC as an Information Security Analyst supporting a Department of Defense client, running a 24×7 security operations center, and at KPMG as a Senior Associate performing penetration tests and information security assessments for Fortune 500 clients. He has served as CISO of Detroit Diesel Corporation, a Daimler Truck North America company, since December 2021.
Kevin Tierney – Executive Director, Global Product Development Quality, General Motors
Kevin Tierney spent more than seven years leading General Motors’ vehicle cybersecurity program before moving into product quality leadership in June 2025. He joined GM’s cybersecurity function as a program manager in April 2013 after an earlier stint at John Deere, where he worked as a Staff Engineer on highly automated and autonomous systems. Tierney advanced through engineering group manager and director roles before becoming GM’s Chief Product Cybersecurity Officer in 2018, then Vice President of Global Cybersecurity in November 2019. During that time, he chaired and vice chaired the Auto-ISAC Board of Directors for six years and served on the CISA Cybersecurity Advisory Committee. He now holds the title of Executive Director, Global Product Development Quality at GM, a role that draws directly on the risk and governance experience he built running the automaker’s cybersecurity program.
Chris Burrows – CISO, Rocket Companies
Chris Burrows built Oakland County, Michigan’s first risk-based information security program from the ground up, a system that protected 82 county divisions, more than 5,000 users, and over 200 applications serving 1.2 million constituents. Before that role, he spent six years as CISO of Holcim US, where he improved information security practices using the ISO 27001/2 framework for 360 North American locations and served on the company’s Global IT Security Standards Board in Zurich. His early career included work as a Unix systems administrator and Oracle database administrator at Detroit Edison, followed by four years running his own consulting practice, Datamation, for government, accounting, automotive, and manufacturing clients. Burrows became CSO of CBI Cyber Security Solutions in 2018 before joining Rocket as CISO in March 2020, where he now leads information security for more than 25,000 team members across Rocket Mortgage, Redfin, Rocket Money, Rocket Close, Rocket Pro, and Rocket Loans. He has been named to Top 100 CISO lists multiple times over the past decade and was recognized as Michigan Government IT Professional of the Year. Outside of cybersecurity, Burrows featured his physical strength in a deadlift video on his profile, an impressive pull of 500 pounds for 13 reps.
Spencer Cremers – CISO, Ally Financial
For five months in 2026, Spencer Cremers held two executive titles at once at Ally, serving as CISO while also acting as interim Chief Information and Data Officer. He joined the company, then known as GMAC, over twenty years ago and built his career entirely inside it, starting as Chief Strategy Officer of the Information Technology Group in 2006. Cremers became CIO of Auto Finance & Insurance in 2008, then CIO of Ally Auto Advantage in 2016, then CIO of Enterprise Technology Operations in March 2020. He stepped into the CISO role in December 2025 and now leads a team of more than 4,000 professionals responsible for securing Ally’s technology and information assets. Before Ally, he spent six years as a Principal Consultant at PwC and nearly four years as a Partner at 4Gen Consulting, both based in Chicago.
Security as a Proving Ground, Not Just a Destination
What separates this group from a typical CISO roster is how many of them used security leadership as a stepping stone to something bigger, not an endpoint. Cremers moved from CIO to CISO to a temporary CIDO appointment inside the same company. Tierney built seven years of cybersecurity credibility at GM before taking that judgment into a product quality role with no security title attached to it. Burrows has layered a COO position at CXO Xchange on top of his CISO work at Rocket since 2024. Even Herrin’s arc, from submarine service to energy insurance to federal cyber policy to a utility company’s top security seat, reads less like a straight line and more like a series of deliberate reinventions. In Detroit, the CISO title increasingly looks like a waypoint in a longer executive career rather than the final stop.
Discover more CISOs securing their organizations:
- Desert Defenders: CISOs to Watch in Phoenix
- Guarding the Triangle: Information Security Leaders to Watch in Raleigh-Durham
- San Diego’s CISOs to Watch: A City That Keeps Its Security Leaders
- Philadelphia’s CISOs to Watch: Securing Health Systems and Heavy Industry
- CISOs to Watch in the Twin Cities: From State Government to the Supply Chain
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.