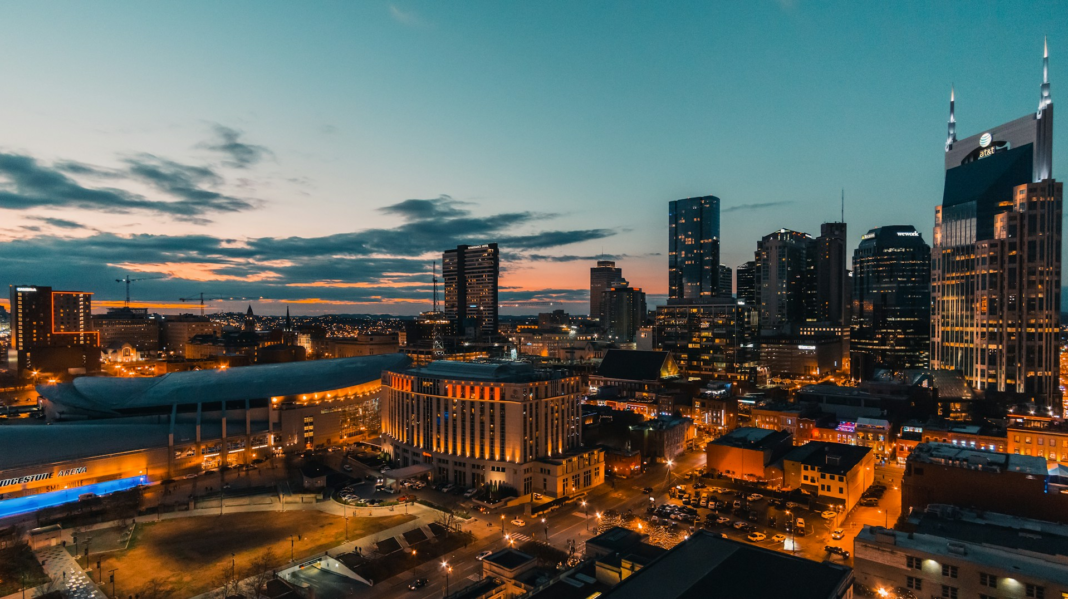
Nashville’s security leadership includes a former FBI cyber agent, a state government executive who has held one job for over a decade, and a healthcare risk leader who spent seven years coordinating outreach programs at a university medical center before ever touching a security role. The routes into these seats vary widely. What holds this group together is the size and complexity of what each person now protects, from a global tire manufacturer’s IoT footprint to the State of Tennessee’s entire technology infrastructure.
Todd Wagner – VP & CISO, Bridgestone Americas
Todd Wagner spent five years investigating computer crimes, terrorism, kidnapping, and white collar crime as an FBI Special Agent before moving into corporate security leadership in 2004. He joined Caterpillar that year and stayed for more than 18 years, working through the company’s information security organization before becoming Director of Global Security in 2017, a converged IT and physical security role covering global response, executive protection, and crisis management. From there he moved into global data privacy leadership, preparing the enterprise for GDPR and CCPA compliance, then built Caterpillar’s IoT compliance program for connected equipment before taking the Segment CISO title for Energy & Transportation in 2022. Wagner joined Bridgestone Americas as Deputy CISO that same year and was promoted to CISO and VP in June 2025, based in Nashville. Before his security career, he worked for nearly five years as Assistant Dean of Students at the University of Toledo, managing campus discipline and orientation programs.
Lee Kaiser – CISO, Highspring
Lee Kaiser led one of the largest enterprise automation and AI programs in the world as Global Head of Operations and System Architecture for Ericsson Group IT, a role spanning 162 countries that delivered more than $850 million in documented enterprise value and earned a World Economic Forum Global Lighthouse distinction. Kaiser joined what is now Highspring in 2023 as Vice President of Infrastructure and Governance, building the compliance foundation that would later support the firm’s security certifications. He was promoted internally to CISO in March 2025 and now owns an $18 million technology budget across security, governance, risk, and compliance, leading a 32-person global organization. Under his leadership, Highspring delivered SOC 2 Type II, ISO 27001, and ISO 27701 certifications concurrently within a single year from a greenfield program, and he built the firm’s first enterprise AI governance framework covering acceptable use policy, deployment controls, and executive decision rights. He also led security and IT carve-out execution for the divestitures of Morgan Franklin Cyber and Pivot Point Consulting. Kaiser serves on the Advisory Board of the Inspire Leadership Network’s Tennessee CISO Chapter.
Curtis Clan – CISO, State of Tennessee
Curtis Clan has spent nearly 24 years inside Tennessee’s state government technology organization, rising from a contracted senior network engineer position in 1997 to the state’s top security role. He joined the state directly as a Senior Network Engineer in 2003, then moved through WAN and data center operations management before becoming Director of Network Services in 2007. Clan has served as Chief Information Security Officer for the State of Tennessee since March 2015, a tenure now past the eleven-year mark. His earlier career included network and systems roles supporting two military medical facilities, Blanchfield Community Army Hospital at Fort Campbell and Keesler Medical Center at Keesler Air Force Base, along with a start as a computer operator at Fort Knox’s Ireland Army Hospital in 1992.
Mark Bruns – SVP & CISO, FirstBank
Mark Bruns has built IT infrastructure and security programs across an unusually wide range of industries, including healthcare, aerospace, automotive, and third-party logistics, over more than 25 years. He worked as IT Director for Gulfstream Aerospace in Savannah, negotiating a multi-million dollar Cisco contract and cutting hardware maintenance costs by half through renegotiated agreements, and later managed IT infrastructure for the Marine Corps’ Semper Fit and Exchange Services Division at Quantico, where he oversaw more than a petabyte of data across multiple storage platforms. Bruns joined naviHealth in 2015 as Director of IT Infrastructure and Information Security, leading a security assessment with Deloitte that produced a three-year roadmap later funded and implemented, including multifactor authentication and penetration test remediation. After a brief stint at Deloitte as an Advisory Manager, he became SVP and CISO at FirstBank in March 2018, a role he has now held for more than eight years. He also serves on the board of the Cyber Risk Institute.
Britton Burton – CISO, D4C Dental Brands
Britton Burton spent seven years coordinating outreach and promotions at Vanderbilt University Medical Center before moving into information security, joining HCA’s risk management team as an Information Protection Analyst in 2013. He advanced to Senior Risk Management Analyst that same year, then became Director of Information Security for HCA’s MidAmerica Division in Kansas City in 2015. Burton returned to Nashville in 2018 as Director of Risk Management, Information Protection and Security at HCA Healthcare, a role he held for four years at one of the largest healthcare systems in the US. He then moved to CORL Technologies in 2022 as Senior Director of Third Party Risk Management and Product Strategy, applying his healthcare risk background to build cybersecurity risk management tools for the broader industry. During that period, he also hosted The CyberPHIx Podcast for Meditology Services, covering cybersecurity news and leading practices for healthcare organizations. Burton has served as CISO of D4C Dental Brands since April 2024.
Different Starting Points, Similar Staying Power
The through-line in this group is tenure. Clan has spent nearly 24 years inside one state government organization. Dell has held two executive titles at the same firm for over two decades. Bruns built his security credibility by working across more industries than most CISOs touch in a career, while Burton did the opposite, building deep expertise in a single sector, healthcare, across three different employers. Wagner is the clearest example of a security career built by accumulation: FBI investigator, then nearly two decades at one industrial manufacturer, then a fresh CISO seat at a second one. Nashville’s security leadership bench was not assembled quickly, and none of these six got here by chance.
Discover more CISOs securing their organizations:
- Guarding the Gateway: Security Leaders to Watch in Miami
- Securing the Motor City: Detroit’s Security Leaders to Watch
- Desert Defenders: CISOs to Watch in Phoenix
- Guarding the Triangle: Information Security Leaders to Watch in Raleigh-Durham
- San Diego’s CISOs to Watch: A City That Keeps Its Security Leaders
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.