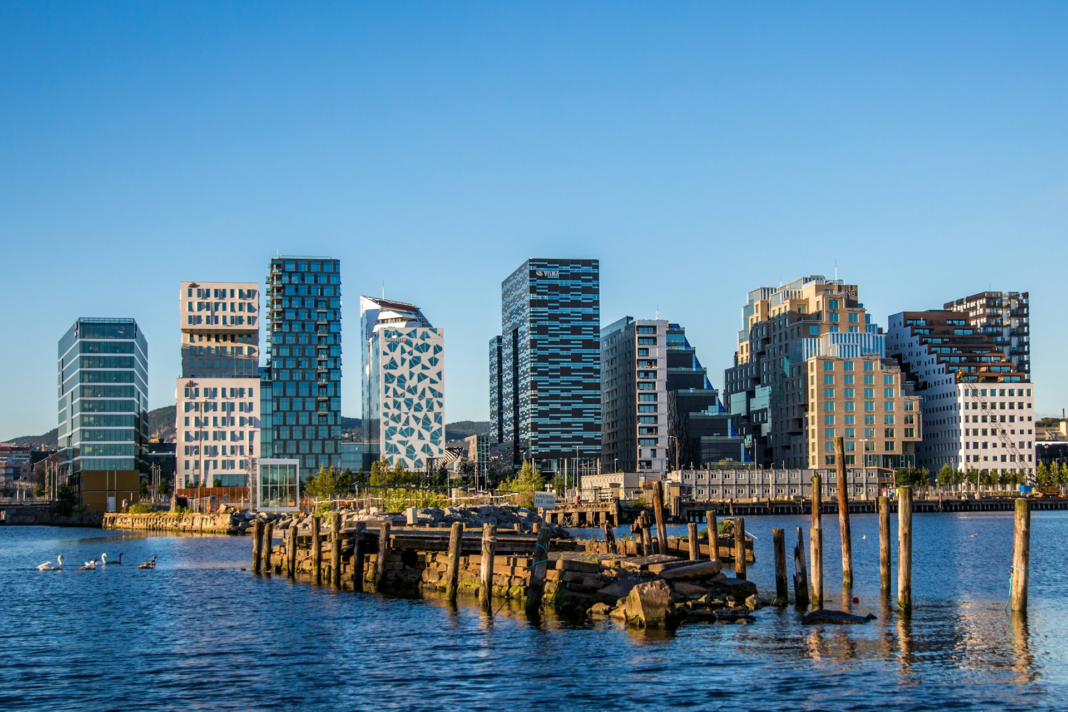
Norway’s cybersecurity leaders arrive from places most security careers never touch. One of the five below negotiated UN access in eastern Afghanistan weeks after the 2001 military offensive and later ran security for humanitarian operations in more than 20 countries. Another audited companies at PwC and ran compliance for a savings bank before he ever held a security title. Others built their careers in security operations centers, antivirus software development, and the CFO’s office. Together they protect a pension and insurance group, an oil company, an industrial technology group, and a renewable power producer, and one is working to widen the field itself.
Stig Torsbakken – CISO, Storebrand
Stig Torsbakken started as a part-time intern doing information security risk analysis at SINTEF, then spent nearly four years at mnemonic as a security consultant and team leader for managed security monitoring. At Nets he moved from technical manager of the security operations center to head of information security operations. He spent five years at Norges Bank Investment Management, leading security operations and then security engineering services. Torsbakken joined Storebrand as CISO in May 2022, and in May 2026 he also took on the role of Chief AI Risk Officer. Having spent his career learning how attackers, technology, and controls work, he now focuses on how executives make decisions, and on changing how cyber risk is communicated so it becomes part of strategy. His view is that organizations systematically underestimate high-consequence, low-probability risks, and that fixing this starts with security professionals.
Sigmund Kristiansen – Chief Cyber Security Officer, Aker BP
Sigmund Kristiansen began as an IT operator at CGGVeritas, then spent more than five years as a software developer at Norman ASA. He moved to DNV in 2007 and spent more than seven years there, finishing as head of section for operational excellence. In 2014 he became Director of Corporate Information Security at Norsk Hydro, leading the function for four and a half years. Kristiansen joined Aker BP as Chief Cyber Security Officer in October 2018 and has held the role for eight years. He sums up his approach as understanding risk, building trust, and delivering improvements, with a focus on enterprise security, digitalization, and communicating risk around technology and AI.
Sindre Stokke – CISO, KONGSBERG
Sindre Stokke came to security from audit and risk management. He worked as an associate and senior associate auditor at PwC, then joined SpareBank 1 as a trainee in 2013, rotating through risk management, finance, and corporate banking. Over the next decade he rose through risk controller and operational risk manager to head of compliance, operational risk, and privacy for SpareBank 1 Sørøst-Norge, also serving as its data protection officer. He became the bank’s head of information security in 2022, overseeing risk management, incident handling, security architecture, and penetration testing. Stokke joined KONGSBERG as CISO in September 2024, where he leads the group’s information and cybersecurity strategy, governance, and security architecture. Before his finance career he was a ski instructor and personal trainer.
Anette Roll Richardsen – President, Women in CyberSecurity (WiCyS) Norway
Anette Roll Richardsen has led WiCyS Norway since 2019, working to bring more expertise, diversity, and new voices into the field. She came to cybersecurity from finance. After roles in credit management and as finance and IT manager at DORMA Norge, she joined Watchcom Security Group as CFO in 2013, became COO, and served as CEO from 2017 to 2023. She then directed cybersecurity at DNV before becoming its global sales director. Since September 2025 she has been a partner at the executive search firm Stanton Chase in Oslo. Richardsen is treasurer of ISACA’s Norway chapter and a board member of the Center for Cyber and Information Security, and SC Media named her one of Europe’s 50 most influential women in cybersecurity.
Glenn Pettersen – VP Security & Emergency Preparedness and CSO, Statkraft
Glenn Pettersen started as a security officer at a Radisson hotel and rose to acting security manager before leaving in 2001 to join the World Food Programme in Afghanistan. As a field security advisor in the country’s eastern region, he assessed the security environment, built local crisis plans, and negotiated access for UN operations. He later commanded a guard platoon at the Norwegian armed forces’ headquarters, served as a liaison and intelligence officer in Kosovo, and helped establish an analysis and intelligence group within the police immigration service. Pettersen spent eight years directing security and emergency preparedness for the Norwegian Refugee Council across operations in more than 20 countries, then led the same function for exploration at Equinor and served as CSO at Höegh LNG. He joined Statkraft as VP Security and Emergency Preparedness and Chief Security Officer in January 2023. He won a Norwegian OSPA award in 2021.
Security Built From Many Directions
Few of Norway’s security leaders followed a single track. Torsbakken and Kristiansen are the closest to traditional paths, one through security operations and the other through software and operational excellence, and both now focus on how risk is understood at the top. Stokke audited companies and ran a bank’s compliance function before security became his job. Richardsen moved from finance into running a security company and now shapes who enters the field. Pettersen spent decades in conflict zones and humanitarian operations before protecting a power producer. In a country where energy, finance, and industry carry national weight, that range of experience is a strength.
Discover more CISOs securing their organizations:
- Keeping the Lines Running: Manufacturing’s Cybersecurity Leaders to Watch
- Brew City’s Cybersecurity Leaders to Watch
- The Crescent City’s Cybersecurity Leaders to Watch
- The Holy City’s Cybersecurity Leaders to Watch
- The Magic City’s Cybersecurity Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.