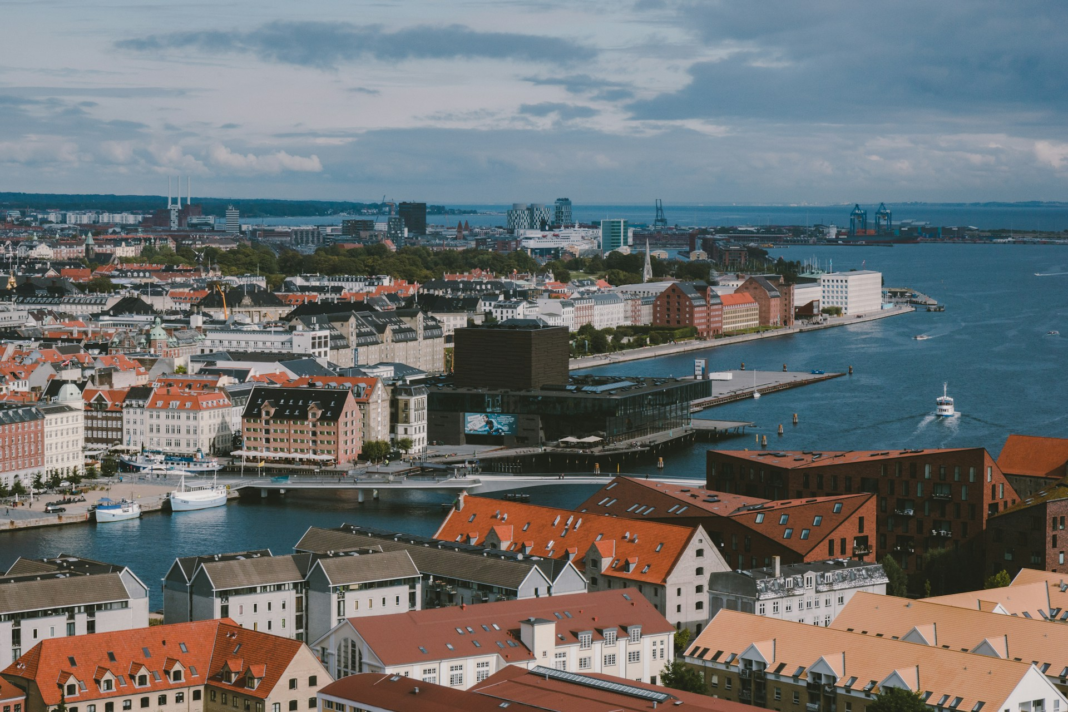
Denmark is a country of fewer than six million people that hosts global companies far out of proportion to its size, and its cybersecurity leaders carry mandates to match. The five below have run security for a pharmaceutical giant, a systemically important bank, the national energy grid, and a global offshore wind company. Their routes in are as varied as their employers: Air Force communications security, IT audit at a cola bottler, Swiss private banking, Unix systems at a U.S. healthcare company, and the law. One spent summers waiting tables on a train through the Alaskan backcountry.
Lars Falch – CISO, VELUX
Lars Falch spent 18 years at Novo Nordisk, more than a decade of them leading its security. He joined from NNIT, where he managed the company’s global laboratory information management system, and spent his first years running quality control and process control systems before directing IT for chemistry, manufacturing, and controls development. He moved into IT security in 2015, added IT quality, and became CISO in 2018, later rising to Corporate Vice President of Global Information Security. In that role he secured Novo Nordisk’s move to the cloud and oversaw security operations, identity, and the security of industrial control systems. Falch left in early 2026 to become a partner at Kopenhagen Konsulting, and since April 2026 has served as CISO for VELUX through the firm. He also advises SECONI and portfolio companies at Primary Venture Partners, and is a member of the AIUC-1 Consortium on secure AI agent adoption. His career began in 1996 supporting telecom and backup products, followed by systems consulting at Unisys and infrastructure projects at Deloitte.
Lance McGrath – Group Chief (Information) Security Officer, Danske Bank
Lance McGrath began as a senior software specialist at Abbott, running Unix systems for research infrastructure and implementing firewalls and VPNs. After a year as technical operations manager at an online gaming startup, he spent more than eight years in Deloitte Switzerland’s cyber risk practice, rising to director. At Credit Suisse in Zurich he served as divisional CISO for International Wealth Management and Corporate Services Technology, and as deputy CISO for the Swiss Universal Bank, where he oversaw a client authentication migration that protected hundreds of thousands of customers. McGrath joined Danske Bank in January 2019 as Group Chief Security Officer, reporting to the COO. He leads more than 400 people across cybersecurity, physical security, technology risk, and operational resilience on a budget above €70 million. He led a multi-year security transformation and closed 11 regulatory orders. Since 2022 he has also served as the bank’s statutory outsourcing officer, and he sits on the board of Nordic Financial CERT.
Jacqueline Johnson – Affiliated Contractor, Valcon
Jacqueline Johnson started as a penetration tester at Ernst & Young, certifying in the firm’s “Extreme Hacking” program. She spent more than eight years at KPMG leading IT audits and its mainframe team across Europe, Africa, and the Middle East, and developed an outsourcing assurance service line. At Nordea she spent six years as Global Head of IT Security, delivering a three-year security program in two and a half years and assessing more than 500 units worldwide against a new information security management system. After leading EY’s Nordic cybersecurity unit and serving as interim deputy CISO for a large Nordic financial institution, she became Group CISO of Ørsted, responsible for IT and OT security globally, where she founded the Security Pledge. She then advised critical infrastructure clients as an associate partner at Implement Consulting before becoming CISO of Energinet in 2022, leading cybersecurity for Denmark’s national energy grid. Since 2024 she has worked independently as an affiliated contractor with Valcon, advising executives and CISOs on operational resilience regulation, AI governance, and board-level risk reporting. Johnson is an attorney with an executive MBA from London Business School, and has spoken at Davos and at Gartner, ISF, and ISACA events.
Karolina Czarkowska – Group VP & CISO, Carlsberg Group
Karolina Czarkowska started in editorial at Reuters before moving into risk with an internship at Deloitte. She spent five years at Coca-Cola HBC working as an internal auditor, IT security manager, and audit manager, then led SAP data migration and process optimization. After leading an SAP team at Infosys, she spent more than five years in global IT audit at HP, Hewlett Packard Enterprise, and Mondelēz International, then advised on technology due diligence and compliance at Deloitte in Warsaw. Czarkowska joined Avon in 2021 to lead global IT governance, risk, and compliance. She became the business unit information security officer for Avon within Natura &Co, and then Avon’s Global CISO. She joined Carlsberg Group as Group VP and CISO in April 2025. She holds an MBA from Warsaw University.
Tania M. Nesser – Head of Global Information Security & Compliance, Coloplast
Tania M. Nesser served 12 years in the U.S. Air Force in communications and information systems, with postings in Washington, South Korea, Italy, Turkey, and Texas. She managed 59 joint-service communications security accounts and served as Computer Emergency Response Team manager for a $25 million network with 2,500 clients. After leaving the service, she spent summers working on Holland America’s rail division in Alaska, putting in 16-hour days serving guests across 450 miles of backcountry per shift. While studying in Denmark she completed security internships at Maersk Drilling, Maersk Tankers, and Maersk Supply Service. Nesser joined Coloplast in 2016 in a temporary one-year role supporting its ISO 27001 certification and never left. She rose through information security risk analyst roles to Head of Global Information Security in June 2024, adding compliance to her remit in November 2025.
Global Mandates From a Small Country
What stands out in Denmark is scale. Falch secured one of the world’s largest pharmaceutical companies for more than a decade. McGrath leads security for a bank whose stability matters to the whole region. Johnson has defended a national energy grid and a global wind power company. Czarkowska and Nesser both protect companies with global operations, one after a career in audit and the other after a career in Air Force communications security. Several of them have also moved between advisory and in-house roles more than once. In a country this size, the same few people end up carrying very large responsibilities, and these five have shown they can.
Discover more CISOs securing their organizations:
- Northern Exposure: Norway’s Cybersecurity Leaders to Watch
- Keeping the Lines Running: Manufacturing’s Cybersecurity Leaders to Watch
- Brew City’s Cybersecurity Leaders to Watch
- The Crescent City’s Cybersecurity Leaders to Watch
- The Holy City’s Cybersecurity Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.