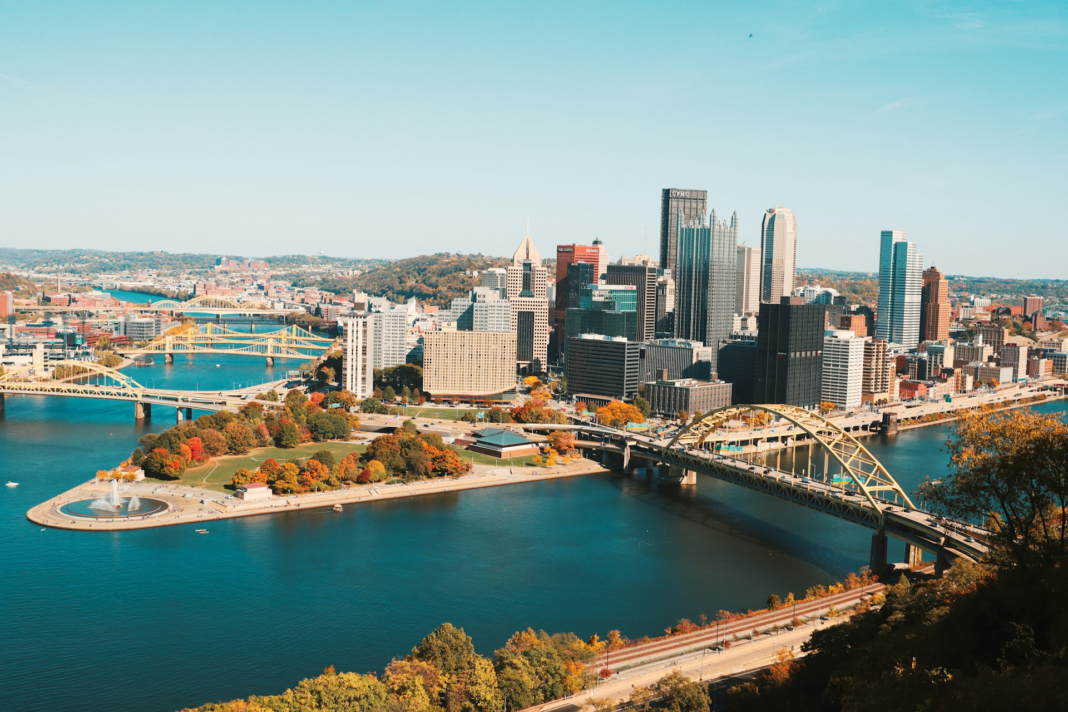
Pittsburgh’s security leadership bench runs deep into the city’s institutional history. One name on this list has worked at the same university for more than 32 years. Another has spent nearly two decades climbing the ranks at the same industrial coatings company. A third built her security career from a co-op position at U.S. Steel, then left to lead security at a competitor before returning to run it at Wabtec. Healthcare, retail, manufacturing, higher education, and heavy industry all draw from the same regional talent pool, and this list moves through each of them.
John Houston – VP, Information Security & Privacy; Associate Counsel, UPMC
John Houston has led UPMC’s information security and privacy function since January 1997, a tenure now approaching three decades at one of the country’s largest integrated health systems. He built an information-centric security program that combines cybersecurity, privacy, data governance, and risk management into a single function, work that led UPMC through HITRUST r2 certification and produced a comprehensive third-party risk management program. His legal background sets him apart from most security executives. As Associate Counsel, Houston negotiates UPMC’s major information technology contracts directly, including electronic health record agreements worth hundreds of millions of dollars. He also served as President of CloudConnect Health IT, a UPMC subsidiary building cloud-based identity management tools for smaller healthcare providers, and spent eight years co-chairing the Subcommittee on Privacy, Confidentiality and Security for the National Committee on Vital and Health Statistics, the statutory advisory body that counsels the Secretary of Health and Human Services on health data policy.
Michael South – VP & CISO, DICK’S Sporting Goods
Michael South leads security for DICK’S Sporting Goods from Reston, Virginia, a remote arrangement for a role formally based in Pittsburgh. Before joining the retailer in January 2025, South spent three years at IBM, rising from Vice President of Infrastructure to Vice President of Cybersecurity and Corporate CISO before a brief stint as VP of Federal IT. His path into corporate security ran through the U.S. Navy and federal government work. He served as CIO and Assistant Chief of Staff for C4I under Commander, Naval Forces Japan, then as Officer in Charge of the Naval Computer and Telecommunications Area Master Station Atlantic in Rota, Spain. After leaving the Navy, he became Deputy CISO and GRC Manager for the Government of the District of Columbia’s Office of the Chief Technology Officer, then spent nearly four years at Amazon Web Services as Americas Regional Leader for Security and Compliance Business Acceleration. South now serves on the board of the Retail & Hospitality ISAC and sits on the National Retail Federation’s IT Security Council. Outside his security career, he founded Dragonfly Travel in 2026, a family travel-planning business built around what the industry calls soft adventure travel.
John O’Rourke – Global CISO, PPG Industries
John O’Rourke has spent his entire 20-year career at PPG Industries, working his way from a systems analyst role into the company’s top security seat. He became Global Chief Information Security Officer in August 2020 after serving as Global IT Director for PPG’s $2 billion Industrial Coatings business, where he completed due diligence and integration planning for two acquisitions worth a combined $220 million. O’Rourke’s earlier roles at PPG included leading the IT integration of two $350 million acquisitions as Senior IT Manager for Coatings Services, and driving the development of a global customer e-commerce portal that now processes more than $1 billion in sales orders annually as Senior IT Manager for Automotive Refinish. Before joining PPG in 2006, he worked as a systems analyst at Pediatrix Medical Group, developing laboratory applications for the medical group’s clinical teams.
John Duska – CISO, University of Pittsburgh
John Duska has worked at the University of Pittsburgh for more than 32 years, a career that began as a Senior Systems Analyst supporting the Registrar’s Office in 1994 and now culminates in the university’s top security role. He became CISO in May 2023 after three years as Deputy CISO, and he reports directly to the university’s Board of Trustees on its security posture. Duska’s earlier work included implementing a PCI DSS compliance program covering 134 point-of-sale locations across three campuses and rolling out EMV chip and point-to-point encryption technology to modernize the university’s payment systems. During his 15 years as Executive Director and Information Security Officer, he also managed the deployment of new point-of-sale terminals across both the university and UPMC, and led his department to become the third organization nationally to earn CompTIA’s Gold-Level A+ Authorized Service Center certification. He serves as the university’s HIPAA Security Officer and is a founding member of the Microsoft Education CISO Council.
Julie Ray – VP & CISO, Wabtec
Julie Ray began her career as an enterprise services co-op student at U.S. Steel in 2002, then spent nearly two decades working her way up through IT operations, network management, and cybersecurity governance roles at the company before becoming CISO in June 2020. She built U.S. Steel’s cybersecurity framework from the ground up using NIST 800-53 standards as Director of Cybersecurity Governance, Risk, and Compliance, work that included developing the company’s identity and access management processes and its cyber compliance reporting program. Ray left U.S. Steel in March 2025 to become VP and CISO at Wabtec Corporation the following month. She also serves as a CISO Coach for Carnegie Mellon University’s Heinz College Executive Education CISO Certificate Program, a role she has held since 2021, and has taught IT and business courses as an adjunct instructor at DeVry University, Point Park University, and the Community College of Allegheny County.
John Johnston – VP & Global CISO, Howmet Aerospace
John Johnston holds three federal security clearances built over a career that moved between corporate security leadership and direct government cyber work. He spent more than two years as a Cyber Security Consultant embedded in the FBI’s Network and Security Operations Center under a contract with Keane Federal Systems, monitoring national cyber threat activity before returning to the private sector. Johnston has held the Chief Security Officer or CISO title at five different companies, including LANXESS Corporation, where he worked with the Department of Homeland Security to help develop the Chemical Facility Anti-Terrorism Standards for the chemical industry, and Westlake Chemical, where he also served as HIPAA Security Officer. He became VP and Global CISO at Howmet Aerospace in May 2022 after a year and a half as Cybersecurity Operations Director at U.S. Steel. Johnston holds a CISSP certification dating back to 2002 and has held a DHS Secret clearance since 2006.
Eris Symms – CISO, United States Steel Corporation
Eris Symms spent more than nine years as CISO at Arconic before taking the same title at United States Steel Corporation in January 2026. Before his promotion to CISO at Arconic in April 2020, Symms worked as the company’s Technical Specialist for more than three years. His earlier career included nearly four years as a Senior Information Systems Engineer at Bechtel Marine Propulsion Corporation, where he administered a VMware View deployment supporting roughly 500 virtualized clients, managed the company’s RSA SecurID authentication environment, and helped deploy Windows 7 to more than 14,000 production desktops using Microsoft System Center Configuration Manager. He also served as Bechtel’s lead BlackBerry Enterprise Server administrator, supporting more than 800 users across the United States and the United Kingdom, and implemented Department of Defense client hardening guidelines across both classified and unclassified networks. Symms has taught as an adjunct professor at Duquesne University and started his career at U.S. Steel itself, working as a help desk agent and business specialist between 1999 and 2007, decades before he would return to lead the company’s security program.
A City That Grows Its Own
The clearest pattern here is internal promotion. Duska spent 32 years working his way through nearly every technical leadership role at the University of Pittsburgh before reaching CISO. O’Rourke did the same at PPG, and Houston has now spent almost three decades building UPMC’s security function from the inside. Even the moves between companies tend to stay close to home. Ray built U.S. Steel’s entire cybersecurity framework before leaving for the CISO seat at Wabtec, and Symms spent nine years running Arconic’s security program before returning to U.S. Steel, the same company where his career started as a help desk agent decades earlier. Johnston is the exception that proves the rule, moving through five different CISO seats across five industries while building a security career that keeps circling back to Pittsburgh. In this city, security leadership looks less like a market and more like a relay.
Discover more CISOs securing their organizations:
- Securing the Bay: Tampa’s CISOs to Watch
- Guarding the Gateway: St. Louis’s Security Leaders to Watch
- Securing Music City: Nashville’s Cyber Leaders to Watch
- Guarding the Gateway: Security Leaders to Watch in Miami
- Securing the Motor City: Detroit’s Security Leaders to Watch
John Kevin Hao is a news and feature writer covering cybersecurity, technology, and business targeted for professional audiences.